
IT & CYBERSECURITY · CLOUD SECURITY
Cloud accounts set up properly, then kept that way.
Most cloud breaches come from a setting nobody reviewed. Cyber6 hardens your Microsoft 365, Google Workspace, Azure, or AWS accounts, plans for recovery, and keeps watch as things change.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
THE PROBLEM
The cloud is safe. The settings often aren't.
When the business moved to Microsoft 365, someone clicked through the setup in an afternoon. Email worked, files synced, and nobody looked at the settings again.
Two years later, a folder of client contracts is shared with anyone who has the link. Three former employees still have active accounts. Activity logging was never switched on, so nobody could say who opened what.
None of this shows up as an error. Everything works. It just works for the wrong people too, and the first sign of a problem is usually someone else finding it.
WHAT IT'S COSTING YOU
Files open to the world
Sharing links set to anyone can be forwarded, indexed, or guessed, exposing client and employee data.
Accounts that never closed
Former staff and old service accounts with active access are an easy way in for attackers.
No record of what happened
Without logging, you can't tell a regulator, insurer, or client what was accessed during an incident.
Recovery that was never planned
Many assume the cloud provider backs everything up. Deleted or encrypted data often isn't recoverable without your own plan.
HOW IT WORKS
How cloud security works
We compare your settings with a known-good starting point, fix what is off, and watch for drift.
STEP 1
Review every setting
Sharing, sign-in, admin roles, guest access, logging, and data retention are compared with a known-good baseline.
STEP 2
Fix in a safe order
Changes are made in stages and explained to your team first, so nobody gets locked out of their work.
STEP 3
Turn on the records
Activity logging and alerts are switched on, so unusual sign-ins and risky changes are recorded and flagged.
STEP 4
Plan for recovery
We agree how quickly each system must come back and how much data you can afford to lose, then test it.
STEP 5
Watch for drift
Settings are monitored continuously, and any change that weakens your baseline is flagged for review.
Review every setting
Fix in a safe order
Turn on the records
Plan for recovery
Watch for drift
WHAT'S INCLUDED
Six ways your cloud accounts stay locked down.
From the first cleanup to a move between services.
- 01
Step 1: Continuous posture monitoring
Microsoft Defender for Cloud watches your cloud accounts for risky settings and changes, and we review what it finds.
WHAT IT MEANS FOR YOU
A risky change is caught in days, not discovered months later.
- 02
Step 2: Settings cleanup
Sign-in, sharing, guest access, admin roles, and logging brought to a known-good baseline and documented.
WHAT IT MEANS FOR YOU
Your files are shared only with the people who should see them.
- 03
Step 3: Structured account setup
A clean layout for Azure or AWS accounts with separate areas for production, testing, and billing, built for growth.
WHAT IT MEANS FOR YOU
Growing in the cloud doesn't mean growing a mess.
- 04
Step 4: Backup and recovery design
Recovery targets agreed with you, your own backups of cloud mail and files, and restores tested on a schedule.
WHAT IT MEANS FOR YOU
A deleted mailbox or encrypted folder can actually come back.
- 05
Step 5: Regulated cloud controls
Cloud settings mapped to HIPAA, SOC 2, an independent security audit, PCI DSS, or CMMC, with evidence saved as you go.
WHAT IT MEANS FOR YOU
Your cloud setup supports your audits instead of complicating them.
- 06
Step 6: Mail and file moves
Moves between Microsoft 365 and Google Workspace, or from an old server, planned so nobody loses mail or a working day.
WHAT IT MEANS FOR YOU
Switching services happens over a weekend, not over a month of disruption.
Services we secure
- Cloud services
- Microsoft 365Microsoft Defender for CloudAzureAWSGoogle Workspace
Running something else in the cloud? We'll confirm coverage during your discovery call.
IN YOUR INDUSTRY
What it looks like in your industry
BEFORE
Agents share transaction folders with anyone who has the link, and the links get forwarded to lenders, inspectors, and relatives.
AFTER
Folders are shared with named people only, links expire, and a report shows who can see each transaction.
WHAT WE MEASURE
What we measure
We score your settings on day one, so every change afterward is measured against where you started.
AIM: GOING UP
Baseline settings met
The share of recommended security settings in place across your cloud accounts.
AIM: GOING DOWN
Files shared publicly
The number of files and folders open to anyone with the link, tracked down over time.
AIM: GOING DOWN
Inactive accounts
Accounts belonging to former staff or unused services that still have access to your data.
AIM: GOING UP
Recovery test results
Whether scheduled restores of cloud mail and files come back complete and within the agreed time.
THE FIRST CLEANUP
Settings we check first
These are the settings most often left open after a quick setup.
- Multi-factor sign-in for every user and every admin
- Sharing links set to named people instead of anyone
- Former staff and unused accounts switched off
- Admin rights limited to the people who need them
- Activity logging switched on and kept long enough
- Your own backups of cloud mail and files
QUESTIONS
Common questions
They secure their services. How your accounts are set up, who can sign in, and what is shared is your responsibility. That is where most problems start.
We make changes in stages and tell your team what to expect first, so nobody suddenly loses access to files they need.
They keep services running, but many deletion and ransomware scenarios aren't covered for long. Your own backups close that gap.
Yes. We plan mail, files, calendars, and accounts, and move them so your team keeps working.
No. Many clients only use Microsoft 365 or Google Workspace. We secure whichever cloud services you actually run.
Continuously. Monitoring flags risky changes as they happen, and we review your overall setup with you on a regular schedule.
Cyber6 is an AI & technology partner. We automate the work slowing businesses down, run and protect their IT, and train their people. Cloud security is part of the Protect work.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Automate · AI & Automation
Automations that read and write to your cloud files use limited, monitored access instead of a shared admin login.
Explore AutomateProtect · IT & Cybersecurity
Cloud security keeps the accounts your business runs on set up correctly as they grow.
You're here
Empower · Training for Businesses & Individuals
Training shows staff how to share files safely, so cleaned-up settings stay that way.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
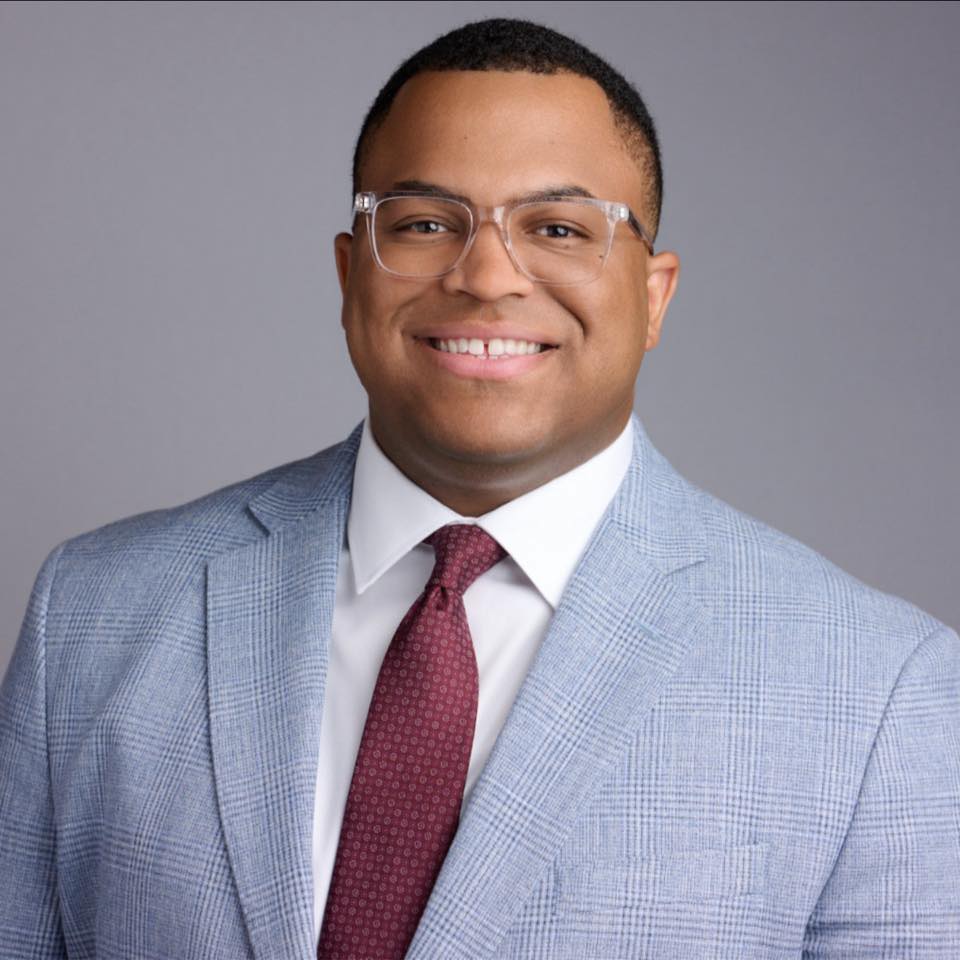
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's lock down your cloud and keep it that way.
A 30-minute call. No cost, no pressure, and honest answers.