
IT & CYBERSECURITY · COMPLIANCE & RISK
Answer the audit, the questionnaire, and the insurer with evidence.
Cyber6 maps where you stand against the rules that apply to you, fixes the gaps in an order that makes sense for your business, and keeps the proof ready for whoever asks next.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
THE PROBLEM
The questionnaire arrives, and nobody knows the answers.
Your largest customer sends a 200-question security questionnaire. It is due in three weeks, and the contract renewal depends on it. Half the questions use words nobody in the office recognizes.
You answer what you can. For the rest, you make your best guess, knowing that a wrong answer could come back to haunt you if something ever goes wrong.
Next quarter, the insurer sends its own form. Then an auditor asks for proof of training. Each request starts from zero, because nothing from the last one was kept in a way anyone can find.
WHAT IT'S COSTING YOU
Lost or delayed contracts
Customers and government agencies increasingly require proof of security before they sign or renew.
Guesses that become liabilities
Answering yes to a control you don't actually have can void insurance coverage or breach a contract.
Fines and findings
Regulated businesses face penalties when an audit or breach reveals required safeguards were never in place.
Hours of repeated effort
Without a system, every audit and questionnaire costs the same scramble as the first one.
HOW IT WORKS
How compliance works with Cyber6
We start with what is actually required of you, not every framework that exists.
STEP 1
Work out what applies
We identify which rules, contracts, and insurer requirements actually apply to your business and your data.
STEP 2
Measure the gap
We compare what you do today against those requirements and write down every gap in plain language.
STEP 3
Fix in priority order
Gaps are ranked by risk and effort, so the most important and quickest fixes happen first.
STEP 4
Collect the evidence
Policies, screenshots, training records, and settings are gathered and kept in one place, updated as things change.
STEP 5
Review vendors
The vendors who hold your data are reviewed, so their weaknesses don't become yours.
STEP 6
Answer with confidence
When the next audit, questionnaire, or renewal arrives, the answers and proof are already ready.
Work out what applies
Measure the gap
Fix in priority order
Collect the evidence
Review vendors
Answer with confidence
WHAT'S INCLUDED
Six pieces that turn requirements into proof.
Use one or all of them, depending on what you are being asked for.
- 01
Step 1: Senior security leadership
We provide a vCISO, a part-time senior security leader who owns your security plan and joins leadership meetings.
WHAT IT MEANS FOR YOU
You get experienced security judgment without a full-time executive salary.
- 02
Step 2: Compliance gap assessment
A clear comparison of where you stand today against the framework you need, with each gap described in plain language.
WHAT IT MEANS FOR YOU
You know exactly what is missing before an auditor tells you.
- 03
Step 3: Evidence collection
Ongoing gathering of policies, settings, and records, organized by requirement and kept current as your business changes.
WHAT IT MEANS FOR YOU
Audits become a review of what you already have, not a scramble.
- 04
Step 4: Vendor risk reviews
Security reviews of the vendors and software providers that store or process your data, repeated on a schedule.
WHAT IT MEANS FOR YOU
A weak vendor is spotted before their problem becomes yours.
- 05
Step 5: AI risk assessment
A review of how the AI tools your team uses handle your data, with clear rules before wider adoption.
WHAT IT MEANS FOR YOU
Staff can use AI tools without putting client data at risk.
- 06
Step 6: Cyber insurance readiness
The controls insurers ask about, checked, put in place, and documented ahead of your application or renewal.
WHAT IT MEANS FOR YOU
Your application answers are true, and you can prove them.
Frameworks we work with
- Frameworks
- NIST CSFNIST 800-53NIST 800-171ISO 27001SOC 2HIPAAPCI DSSCMMC
- Evidence tracking
- SecureFrame
Working toward a different standard? Tell us on your discovery call.
IN YOUR INDUSTRY
What it looks like in your industry
BEFORE
A defense contract requires CMMC, and the company doesn't know which of the requirements it already meets.
AFTER
A gap assessment lists each requirement, what is in place, and what is missing, with a plan to close the gaps in order.
WHAT WE MEASURE
What we measure
We record your starting position during the gap assessment, so every step forward is visible.
AIM: GOING UP
Requirements met
The share of requirements in your framework that are fully in place and backed by evidence.
AIM: GOING DOWN
Open gaps by risk
The number of remaining gaps, sorted by how much risk each one carries for your business.
AIM: GOING UP
Evidence freshness
How much of your stored evidence is current, compared with items that are out of date or missing.
AIM: GOING DOWN
Questionnaire turnaround
How long it takes to answer a customer or insurer questionnaire, from arrival to submission.
WHAT YOU'LL HAVE
At the end of the first phase
These are the documents you can hand to an auditor, customer, or insurer.
- A list of the rules and requirements that apply to you
- A written gap assessment in plain language
- A prioritized plan with owners and dates
- Security policies that match how you actually work
- A folder of evidence organized by requirement
- A list of key vendors and when each was last reviewed
QUESTIONS
Common questions
It depends on your data, customers, and contracts. We start by working out what actually applies to you, which is often fewer than people expect.
No. We prepare you for it and support you through it. An independent auditor issues the report or certification.
We help you answer it truthfully, using evidence you actually have. We won't mark a control as in place when it isn't.
They own your security plan, report progress to leadership, answer tough questions from customers and auditors, and make decisions on risk.
It depends on the framework and your starting point. The gap assessment gives you a realistic plan with dates.
No. Compliance proves you meet a set of rules. We use it as a structure for real protection, not as paperwork for its own sake.
Cyber6 is an AI & technology partner. We automate the work slowing businesses down, run and protect their IT, and train their people. Compliance is part of the Protect work.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Automate · AI & Automation
Automations that touch client or patient data are reviewed against your requirements before they go live.
Explore AutomateProtect · IT & Cybersecurity
Compliance turns the protections you have into proof that others will accept.
You're here
Empower · Training for Businesses & Individuals
Required staff training is delivered and recorded through Cyber6 Academy, ready for your evidence folder.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
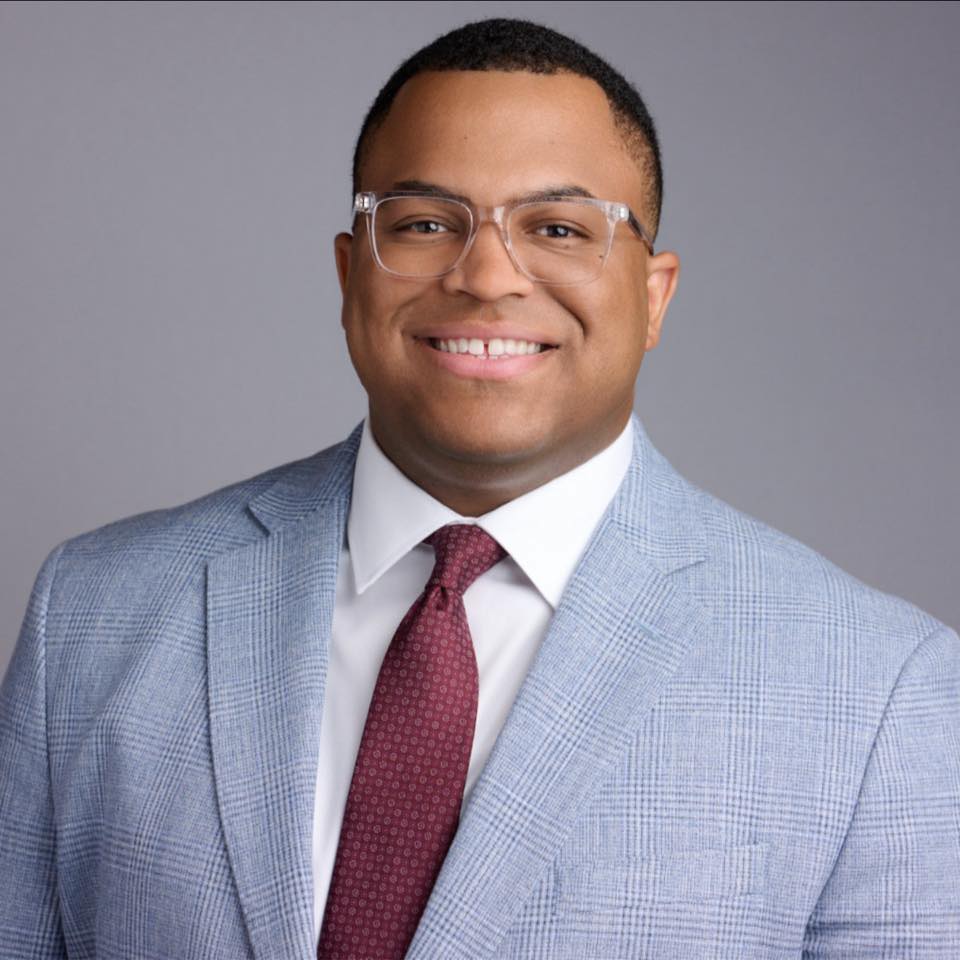
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's get your answers ready before the next request.
A 30-minute call. No cost, no pressure, and honest answers.