
SOLUTION · IT & CYBERSECURITY
Ransomware protection.
Ransomware locks your files and holds them for payment, and it often steals a copy first. We make it hard to get in, catch it fast if someone tries, and make sure you can get back to work without paying.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
WHAT'S REALLY HAPPENING
How an attack usually happens
Ransomware rarely announces itself ahead of time. It usually starts with one ordinary click on an otherwise normal-looking day.
STEP 01
An email looks normal
Someone on your team opens an email that looks like an invoice, a shipping notice, or a shared document. It looks routine, so they click.
STEP 02
The attacker gets in quietly
Sometimes it's a stolen password instead of an email. Either way, the attacker is now inside and nobody has noticed.
STEP 03
They look around for days or weeks
The attacker maps your network, finds your important files, and finds your backups, all without triggering an alarm because nobody is watching.
STEP 04
Data is copied and files are locked
They copy your data, then lock your files and try to destroy your backups so you have no way back except paying.
STEP 05
A demand appears on your screens
By Monday morning, a message demands payment, and invoicing, scheduling, and payroll are all stopped.
WHY IT HAPPENS
Four gaps behind almost every ransomware attack.
Select a cause to see the problems it creates in your business.
- Password-only logins: A stolen or guessed password is enough to get in when there's no second step required. Leads to: Attacker gets in, Repeat attempts.
- No one watching after hours: Most attacks happen at night or on weekends, when nobody is looking at alerts. Leads to: Spreads unseen, Attacker gets in.
- Backups never tested: A backup that has never been restored might not work when you need it, or might be reachable by the attacker. Leads to: No recovery, Legal exposure.
- Untrained staff: Without training, a convincing fake email or attachment is hard to tell apart from a real one. Leads to: Attacker gets in, Repeat attempts.
A stolen or guessed password is enough to get in when there's no second step required.
Attacker gets inRepeat attempts
WHO IT HITS HARDEST
Where ransomware hits the hardest.
SCENARIO
Medical practices
Patient records are a prime target, and downtime stops care instead of just slowing it.
See the medical practices pageMedical practices
Patient records are a prime target, and downtime stops care instead of just slowing it.
Industry pageLaw firms
Attackers steal client files first, then threaten to publish them if payment doesn't come.
Industry pageManufacturing
Old plant-floor computers and shared networks let an attack stop production for days.
Industry pageLocal government
Small IT teams and legacy systems make public services a frequent, visible target.
Industry pageSIGNS THIS IS HAPPENING TO YOU
Six questions show how exposed you are.
One question at a time. The gauge moves as you answer.
Does every login require a second step beyond a password?
EXPOSURE
0 gaps so far
This runs in your browser only. Nothing you choose is sent anywhere.
WHAT IT'S COSTING YOU
What an attack costs, even without paying.
LINE ITEM
CATEGORY
- 01MONEY
Work stops
You may not be able to invoice, schedule, take payments, or run payroll until systems are restored.
- 02MONEY
Recovery is expensive even without paying
Cleanup, rebuilding computers, and restoring data take time and outside help, even if you never pay a ransom.
- 03COMPLIANCE
Notification and legal exposure
If customer or patient data is stolen, you may be legally required to notify them, and face questions from regulators and clients.
- 04MONEY
Insurance gets harder
Some businesses find their cyber insurance premiums go up or coverage gets harder to get after an incident.
- 05REPUTATION
Trust takes a hit
Customers and partners remember who was offline for a week. Some quietly move their business elsewhere.
HOW CYBER6 FIXES IT
Layers that stop an attack at each stage.
IT & Cybersecurity does most of the work here. Training closes the gap where people are the target. Select any piece to see what it does.
IT & CYBERSECURITY
Stop it at the inbox
We filter every email for fake invoices, dangerous attachments, and lookalike senders before they reach your team.
WHAT IT MEANS FOR YOUFar fewer dangerous emails ever land in front of your staff.
TRAINING
- IT & CYBERSECURITY: Stop it at the inbox. We filter every email for fake invoices, dangerous attachments, and lookalike senders before they reach your team. Far fewer dangerous emails ever land in front of your staff.
- IT & CYBERSECURITY: Make stolen passwords useless. A second step on login, like approving a prompt on your phone, is added to email, remote access, and key business systems. A stolen password alone can't get an attacker in.
- IT & CYBERSECURITY: Stop it on the computer. Software on every device watches for suspicious behavior, like a program locking hundreds of files, and stops it, and can undo the damage. An attack can be stopped in its tracks instead of spreading.
- IT & CYBERSECURITY: Watch around the clock. A [[soc|security operations center]] monitors your environment 24/7, including nights and weekends, when attacks often happen. Someone is paying attention when you're not.
- IT & CYBERSECURITY: Backups you can count on. Important data is backed up, kept separate from your network so attackers can't reach it, and tested to confirm it restores. If the worst happens, you can recover without paying.
- TRAINING: Train your team to spot it. Short, practical training and realistic practice phishing emails, plus a leadership exercise on what to do in an attack. Your people become an early warning system instead of the weak link.
WHAT'S INCLUDED
Everything we set up, in the order we set it up.
Six pieces, set up in this order during your first weeks.
01
Risk assessment
A plain-English review of where you're exposed today.
02
Email filtering
Fake invoices, dangerous attachments, and lookalike senders get caught before they land.
03
Multi-factor authentication
A second login step on email, remote access, and key business systems.
04
Endpoint protection
Software on every device that stops and can undo suspicious activity.
05
Tested backups
Daily backups, kept separate from your network, restored on a test schedule.
06
Staff training
Practical sessions and simulated phishing emails, plus a leadership exercise.
BEFORE AND AFTER
A ransomware attempt, two ways.
| A typical Monday without Cyber6 | A typical Monday with Cyber6 |
|---|---|
| Password-only logins | A second step on every login |
| Backups nobody has tested | Backups kept separate and tested regularly |
| No one watching after hours | 24/7 monitoring |
| Staff guessing which emails are safe | Trained staff and filtered inboxes |
| Updates happen when someone remembers | Updates managed and tracked |
| No plan if something happens | A written plan and a team ready to act |
NO PROTECTION IS PERFECT
If something happens anyway
No protection can promise nothing will ever get through. What matters is how fast it's caught and how well you recover.
- 1
Detect
Our systems and team spot unusual activity.
- 2
Contain
We cut the affected devices off from the network so it can't spread.
- 3
Recover
We remove the threat and restore from clean backups.
- 4
Report
We help you meet notification obligations and work with your insurer and legal counsel.
- 5
Learn
We review what happened and close the gap.
WHAT WE MEASURE
Four numbers you'll see every month.
We record a starting point during onboarding and report on these every month.
EVERY MEASURE IS TRACKED THROUGH THE CYBER6 PROVE FRAMEWORK
- Plan the goals
- Record the baseline
- Operate and observe
- Verify the results
- Evolve
PLAN THE GOALS
Time to detect
How long between suspicious activity starting and it being flagged.
RECORD THE BASELINE
Restore tests passed
Whether scheduled backup restores completed and the data was usable.
OPERATE AND OBSERVE
Devices with endpoint protection
The share of computers and servers with active protection software.
VERIFY THE RESULTS
Phishing report rate
How many simulated phishing emails staff correctly reported.
IN YOUR INDUSTRY
What changes in your industry
BEFORE
Patient scheduling and records freeze during an attack, and appointments have to be cancelled.
AFTER
Layered protection and tested backups keep patient care running, and records are restored quickly if something gets through.
Medical practices pageWHY CYBER6
Why Cyber6 for ransomware protection
01
Layers, not one control
Email filtering, MFA, endpoint protection, and backups work together, so one gap doesn't become the whole story.
02
Watching when you're not
24/7 monitoring catches activity at the times attacks most often happen.
03
Backups that are proven to work
We test restores on a schedule instead of hoping a backup works when you need it.
04
Training that sticks
Practical, recurring training turns your team into an early warning system.
QUESTIONS
Questions people ask
We don't recommend it. Paying doesn't guarantee you'll get your data back or that it won't be published, and it can mark you as a target. That decision should involve your legal counsel, your insurer, and law enforcement.
No. Many attacks are automated and go after any business with weak spots. Smaller businesses are often targeted because they have fewer defenses.
They keep the service running, but protecting your data from deletion, mistakes, and ransomware is your responsibility. Their built-in retention isn't designed to be a full backup.
The protection software is built to run in the background. Most people don't notice it.
Often yes. We can work alongside your IT person and handle the 24/7 monitoring and security tools that are hard for one person to cover.
Not necessarily. We'll review what you have and only recommend changes where there's a real gap.
It depends on your size and setup. We start with the biggest risks first so you're better protected quickly, then complete the rest in phases.
We contain the affected systems, remove the threat, and restore from backups that are kept separate from your network.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Protect · IT & Cybersecurity
IT and cybersecurity, managed around the clock.
You're here
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
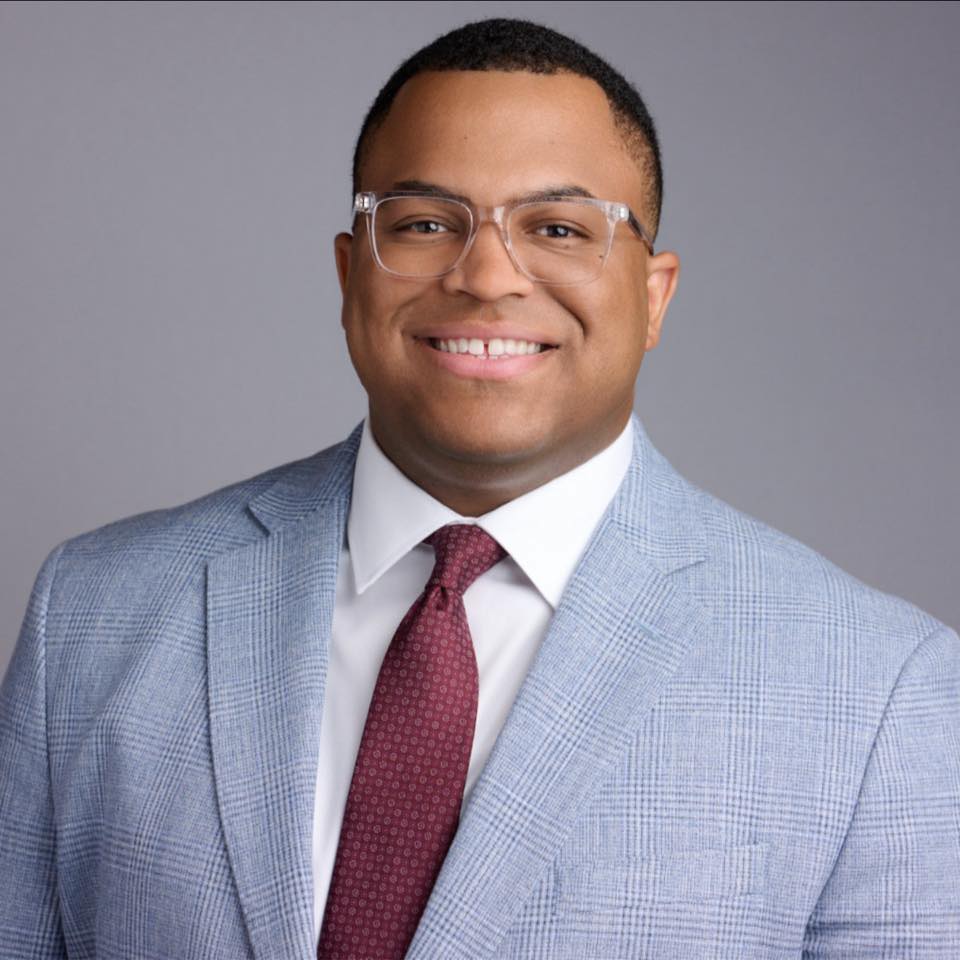
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's find your weak spots before someone else finds them for you.
A 30-minute call. No cost, no pressure, and honest answers.