
SOLUTION · IT & CYBERSECURITY
Compliance requirements.
A questionnaire or an audit request lands, and you have some of the pieces but nothing written down as a whole. Cyber6 finds out what actually applies to you, closes the gaps, and keeps the evidence ready.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
WHAT'S REALLY HAPPENING
How a compliance request turns into a scramble
It rarely starts with a violation. It starts with a request nobody was ready for.
STEP 01
A questionnaire or audit request arrives
A customer, insurer, or regulator sends a security questionnaire, and someone has to answer it fast.
STEP 02
You realize the pieces exist, but not as a whole
A password policy here, a firewall rule there, but nothing written down together as one program.
STEP 03
Someone spends days pulling evidence from memory
Screenshots, old emails, and half-remembered settings get gathered under deadline pressure, with no central record to check against.
STEP 04
A follow-up question exposes a gap
The first answers go in, and a follow-up question about a control nobody had actually tested stalls the review.
STEP 05
The contract stalls, or the finding repeats
A renewal or a deal waits on an answer that isn't ready, or the same audit finding shows up again next year because nothing changed.
WHY IT HAPPENS
Four causes sit behind almost every compliance scramble.
Select a cause to see the problems it creates when a request lands.
- No one owns compliance evidence: When evidence collection is nobody's job, an audit becomes a rushed search through email and shared drives. Leads to: Scrambled evidence, Wasted hours, Stalled contracts.
- Nobody knows which framework applies: Guessing at requirements means working against the wrong list, or no list at all, until a questionnaire forces the question. Leads to: Stalled contracts, Lost deals.
- Policies exist but aren't followed: A written policy that doesn't match daily practice gives false confidence and leaves the real risk in place. Leads to: False confidence, Repeat findings.
- Vendors are never reviewed: A vendor holding your data with weak security of its own becomes your problem the moment something goes wrong. Leads to: Repeat findings, False confidence.
When evidence collection is nobody's job, an audit becomes a rushed search through email and shared drives.
Scrambled evidenceWasted hoursStalled contracts
WHO IT HITS HARDEST
Where compliance pressure hits the hardest.
SCENARIO
Office and practice managers
They get handed a 40-page questionnaire with a deadline and no owner for most of the answers.
Office and practice managers
They get handed a 40-page questionnaire with a deadline and no owner for most of the answers.
Medical practices
HIPAA requires a documented risk assessment and evidence an auditor can actually see.
Industry pageSaaS and technology companies
Enterprise buyers routinely require a completed SOC 2 review before they'll sign.
Industry pageDefense contractors
For defense contractors, CMMC and NIST 800-171 compliance is a condition of holding the contract at all.
Industry pageSIGNS THIS IS HAPPENING TO YOU
Six questions show how exposed you are.
One question at a time. The gauge moves as you answer.
Do you know which framework or contract requirements actually apply to you?
EXPOSURE
0 gaps so far
This runs in your browser only. Nothing you choose is sent anywhere.
WHAT IT'S COSTING YOU
Poor compliance readiness adds up to real losses.
LINE ITEM
CATEGORY
- 01MONEY
Stalled contracts
A security questionnaire that sits unanswered can hold up a signature you're waiting on.
- 02REPUTATION
Repeat audit findings
The same gap flagged year after year signals to auditors and customers that nothing changed.
- 03TIME
Scrambled evidence every time
Without ongoing collection, every request turns into a rushed search through email and shared drives.
- 04RISK
Real gaps hiding behind paperwork
A policy that isn't followed gives false confidence and leaves the actual risk in place.
- 05MONEY
Lost deals
Enterprise and government buyers increasingly require a completed security review before they'll sign.
HOW CYBER6 FIXES IT
One team finds the gaps and keeps evidence ready.
IT & Cybersecurity does most of the work here, from assessment to testing. Select any piece to see what it does.
IT & CYBERSECURITY
Find out what actually applies
We review your industry, your data, and your contracts to identify which frameworks matter, such as , SOC 2, PCI DSS, or CMMC for defense contractors.
WHAT IT MEANS FOR YOUYou stop guessing which rules apply and start working against the right list.
TRAINING
- IT & CYBERSECURITY: Find out what actually applies. We review your industry, your data, and your contracts to identify which frameworks matter, such as [[hipaa|HIPAA]], SOC 2, PCI DSS, or CMMC for defense contractors. You stop guessing which rules apply and start working against the right list.
- IT & CYBERSECURITY: Run a gap assessment. We compare your current controls and documentation against the framework, item by item, and give you a plain list of what's missing. You see exactly what to fix, in order of risk.
- IT & CYBERSECURITY: A fractional security lead. A part-time security lead sets priorities and represents your security posture to auditors and customers, without a full-time salary. You get experienced judgment on hard calls without carrying a full-time hire.
- IT & CYBERSECURITY: Continuous evidence collection. We track evidence, like access reviews and training completion, as it happens instead of scrambling once a year. When an audit or questionnaire arrives, the evidence is already there.
- IT & CYBERSECURITY: Vendor security reviews. We track which vendors have access to what, request their own security documentation, and flag any that pose outsized risk. A vendor's weak security doesn't quietly become your breach.
- IT & CYBERSECURITY: Testing that confirms controls work. Testers try to get past the same defenses an attacker would target, and the findings go straight into your compliance evidence. You find the real gap before an auditor or an attacker does.
- TRAINING: Short staff training. Brief sessions show staff what evidence looks like day to day, like reporting an incident or completing required training. Fewer findings come from staff not knowing what's expected.
WHAT'S INCLUDED
Everything we set up, in the order we set it up.
Six pieces, set up in this order once you start.
01
Framework identification
We review your industry, data, and contracts to find out which requirements actually apply.
02
Gap assessment
A plain-English list of what's missing, ranked by risk.
03
Written policies
A written information security policy and the documents it requires.
04
Evidence collection
Ongoing tracking of access reviews, training, and system logs.
05
Vendor review process
A schedule for reviewing vendors that hold or touch your data.
06
Testing
Penetration testing that confirms your controls hold up in practice.
BEFORE AND AFTER
An audit request, two ways.
| A typical Monday without Cyber6 | A typical Monday with Cyber6 |
|---|---|
| Nobody owns compliance evidence | A named fractional security lead owns the program |
| Documents scattered across email and drives | Evidence tracked in one place, continuously |
| Unsure which framework applies | A clear list of requirements that actually apply |
| Vendor risk untracked | Vendors reviewed and ranked by risk |
| Audit findings repeat every year | Findings closed and verified |
| Policies exist but aren't followed | Controls tested to confirm they work |
| A questionnaire sits unanswered for weeks | Answers come from evidence already on hand |
NO PROTECTION IS PERFECT
How it works day to day
Compliance isn't a single event. Here's how the ongoing work runs once it's set up.
- 1
Collect
Access reviews, training records, and system logs are gathered on a set schedule.
- 2
Review
Your fractional security lead checks for gaps or expiring evidence before they become a problem.
- 3
Check vendors
Vendors with access to your data are reviewed on a rolling schedule, not just at contract renewal.
- 4
Respond
When a customer or insurer sends a questionnaire, we answer it from the evidence already on hand.
- 5
Reassess
We reassess the framework and your controls at least yearly, or after a major change to your business.
WHAT WE MEASURE
Three numbers you'll see every review.
We record a starting point during the assessment and report on these on a set schedule.
EVERY MEASURE IS TRACKED THROUGH THE CYBER6 PROVE FRAMEWORK
- Plan the goals
- Record the baseline
- Operate and observe
- Verify the results
- Evolve
PLAN THE GOALS
Gaps closed
How many findings from the gap assessment have been fixed and verified.
RECORD THE BASELINE
Evidence collected on schedule
The share of required evidence gathered on time instead of chased down late.
OPERATE AND OBSERVE
Vendors reviewed
How many vendors with access to your data have a current security review on file.
IN YOUR INDUSTRY
What changes in your industry
BEFORE
A HIPAA risk assessment was done once, years ago, and nobody can produce current evidence for an auditor.
AFTER
A current risk assessment and tracked evidence are ready whenever a patient, partner, or regulator asks.
Medical practices pageWHY CYBER6
Why Cyber6 for compliance
01
We find out what actually applies
We identify the real requirements from your industry and contracts instead of assuming a generic list.
02
A named lead, not a binder of policies
A fractional security lead owns the program and answers hard questions from auditors and customers.
03
Evidence collected continuously
Evidence is tracked as it happens, so an audit stops being a scramble.
04
Testing backs up the paperwork
Penetration testing confirms your controls actually hold up, not just that they're written down.
QUESTIONS
Questions people ask
It depends on your industry, the data you hold, and what your contracts and insurers require. We identify this during the assessment rather than guessing up front.
Most small and mid-sized businesses don't need one full time. A fractional lead gives you the same leadership on a schedule that fits your size.
It depends on the framework and your size, but you'll get a prioritized list of findings, not just a long report to interpret on your own.
Yes. We often start there, since it's usually the most immediate pressure, and build the ongoing program from what that review requires.
We help you respond, fix the gap, and document the remediation. Auditors generally look for a real plan, not perfection.
No. SOC 2, PCI DSS, and customer security addendums apply well beyond healthcare, especially for SaaS and technology companies.
Yes, as part of the same engagement, so testing results feed directly into your compliance evidence.
We review what exists first. We only rewrite what's actually outdated or incomplete.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Protect · IT & Cybersecurity
IT and cybersecurity, managed around the clock.
You're here
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
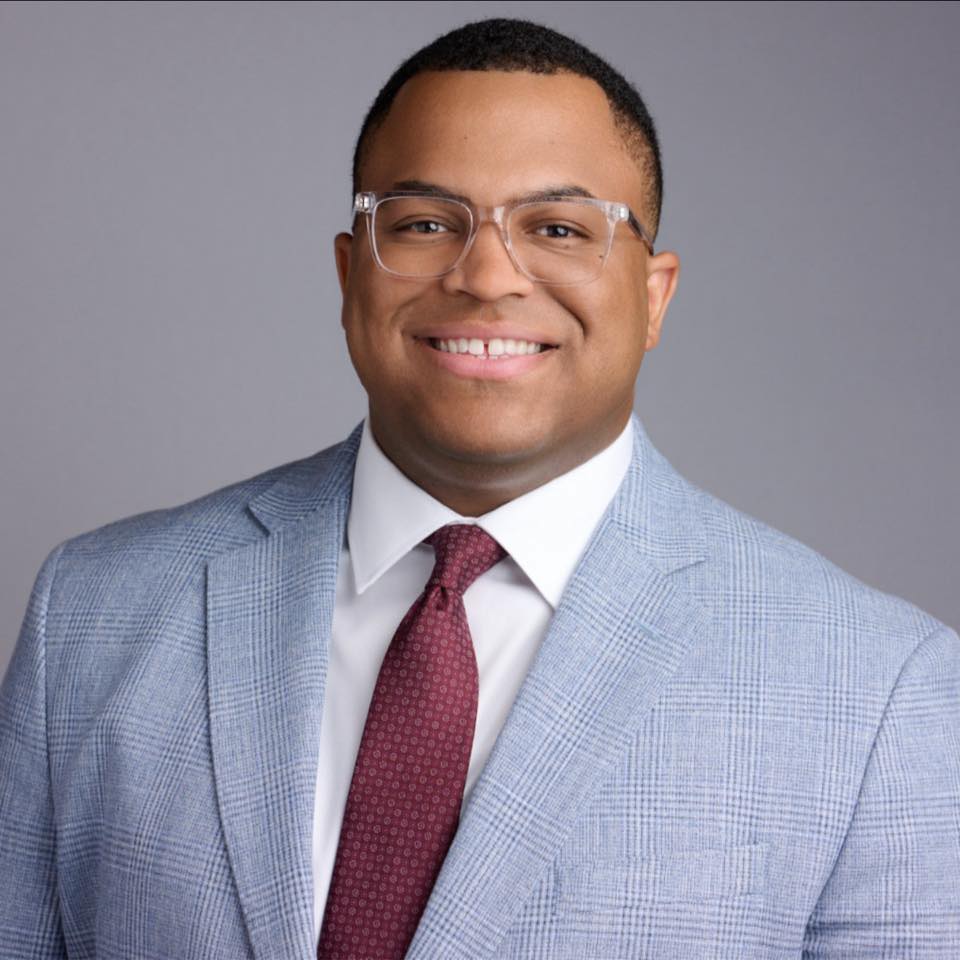
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's get your evidence ready before someone asks for it.
A 30-minute call. No cost, no pressure, and honest answers.