
SOLUTION · TRAINING
Safe AI use.
Your team is already using AI tools with company and client data, and nobody wrote the rules. We help you decide what's safe, put guardrails around the rest, and train your team so good work keeps going.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
WHAT'S REALLY HAPPENING
How the risk usually shows up
It rarely starts with bad intentions. It starts with a deadline and a free tool that seems harmless.
STEP 01
A deadline creates a shortcut
An employee is behind schedule and pastes a client contract into a free AI tool to get a fast summary. Nobody told them not to, because there's no written policy.
STEP 02
More staff do the same thing
One person's shortcut becomes a habit across the team. Spreadsheets, emails, and client notes all start flowing into personal AI accounts on work laptops.
STEP 03
The data is already out of your hands
The free tool's terms allow it to use submitted text to improve its models. Client names, financial details, and health information are now on a server you don't control.
STEP 04
Fear leads to an all-or-nothing reaction
Someone notices the risk and reacts by banning AI outright. Staff who were using it carefully lose real time savings, and the ones using it carelessly just switch to their phones.
STEP 05
A client asks the question you can't answer
A security questionnaire or a new contract asks exactly how your business reviews and controls AI use. There's no policy, no record, and no ready answer.
WHY IT HAPPENS
Four causes sit behind most AI data exposure.
Select a cause to see the problems it creates for your business.
- No written policy: Nobody has said, in plain words, what can and can't go into an AI tool. Staff are left to guess, and guesses go different ways. Leads to: Data outside your control, Inconsistent use.
- Personal accounts on work devices: Staff sign into free, personal AI accounts on company laptops because no approved business option was ever set up. Leads to: Data outside your control, Confidentiality risk.
- No technical guardrails: Nothing scans or blocks sensitive data heading to an unapproved tool, so a mistake goes through every time. Leads to: Confidentiality risk, Failed questionnaires.
- Fear-driven bans: Without a plan, leaders sometimes ban AI outright rather than manage the risk, which gives up real time savings and pushes use underground. Leads to: Lost time savings, No documentation.
Nobody has said, in plain words, what can and can't go into an AI tool. Staff are left to guess, and guesses go different ways.
Data outside your controlInconsistent use
WHO IT HITS HARDEST
Where unmanaged AI use hurts the most.
SCENARIO
Law firms
Pasting client material into an outside tool can raise real confidentiality questions tied to professional duty.
See the law firms pageLaw firms
Pasting client material into an outside tool can raise real confidentiality questions tied to professional duty.
Industry pageAccounting and tax practices
Deadline pressure during filing season is exactly when staff reach for the fastest tool available.
Industry pageProfessional services firms
Client contracts, proposals, and financial data move through daily work, with no policy to say where the line is.
Technology companies
Source code and customer data are tempting to summarize or debug with an outside AI tool.
Industry pageSIGNS THIS IS HAPPENING TO YOU
Six questions show how exposed you are.
One question at a time. The gauge moves as you answer.
Do you have a written policy on which AI tools staff can use?
EXPOSURE
0 gaps so far
This runs in your browser only. Nothing you choose is sent anywhere.
WHAT IT'S COSTING YOU
Unmanaged AI use adds up to real risk.
LINE ITEM
CATEGORY
- 01RISK
Client data leaves your control
Once information is submitted to a consumer AI tool, you can't verify it was deleted or confirm who can see it.
- 02RISK
Confidentiality exposure
For law firms and advisors, pasting client material into an outside tool can raise real confidentiality questions.
- 03MONEY
Failed questionnaires and lost contracts
Clients increasingly ask how you handle AI in security questionnaires. A missing policy can hold up or lose a deal.
- 04TIME
Good use gets shut down with the bad
Some businesses respond to the risk by banning AI outright, giving up real time savings out of fear instead of managing it.
- 05REPUTATION
Inconsistent practice across the team
One person is careful, another isn't, and nobody set the expectation either way. That's hard to defend if something goes wrong.
- 06COMPLIANCE
No record to point to
Without a documented policy and training log, there's nothing to show a client, an auditor, or an insurer who asks.
HOW CYBER6 FIXES IT
Policy, guardrails, and training work together.
Training and IT & Cybersecurity carry most of this page. AI & Automation puts safe use to work once the guardrails are in place. Select any piece to see what it does.
TRAINING
Plain-language AI policy
We write a policy that says, in real sentences and real examples from your business, what can and can't go into which tools.
WHAT IT MEANS FOR YOUStaff know exactly where the line is instead of guessing.
IT & CYBERSECURITY
AI & AUTOMATION
- TRAINING: Plain-language AI policy. We write a policy that says, in real sentences and real examples from your business, what can and can't go into which tools. Staff know exactly where the line is instead of guessing.
- TRAINING: Staff training on real examples. Short sessions walk through what's fine to paste into an AI tool, what isn't, and why the difference matters for your clients. Your team makes the right call in the moment.
- IT & CYBERSECURITY: Data loss prevention on AI tools. Technical rules catch client records or financial data before they're submitted to an unapproved tool. A guardrail catches the mistake even if someone forgets the policy.
- IT & CYBERSECURITY: Approved business accounts. For the AI tools your team needs, we set them up so data stays inside your organization's account instead of a personal one. Your team gets the benefit of AI without the data walking out the door.
- IT & CYBERSECURITY: Documentation for clients and auditors. A record of your policy, approved tools, and completed training, ready to hand over. One less thing holding up a contract or a renewal.
- AI & AUTOMATION: Reviewed drafting assistants. Where AI can save real time, like drafting a first version of a document, we build it into the workflow with a person reviewing the output. Time savings, with a person still in charge of what goes out the door.
WHAT'S INCLUDED
Everything we set up, in the order we set it up.
Six pieces, set up in this order.
01
Tool review
We look at which AI tools your staff already use and where sensitive data might already be exposed.
02
Policy draft
A plain-language AI acceptable-use policy, written with your business's real examples.
03
Approved tool list
A reviewed list of which AI tools are approved, restricted, or replaced.
04
Technical controls
Data loss prevention rules that catch sensitive data heading to an unapproved tool.
05
Staff training
Short sessions with real examples so staff know where the line is.
06
Documentation and review schedule
A record of the policy and training, reviewed on a regular schedule as new tools appear.
BEFORE AND AFTER
A typical week, two ways.
| A typical Monday without Cyber6 | A typical Monday with Cyber6 |
|---|---|
| No written AI policy | A plain-language policy everyone has read |
| Personal AI accounts on work devices | Approved business accounts with data kept in your control |
| No way to catch sensitive data leaving | Technical rules that block or flag it |
| Staff guessing what's allowed | Staff trained on real examples |
| AI banned out of fear, or unmanaged out of habit | AI used where it helps, with guardrails in place |
| No answer for a client's security questionnaire | A documented policy and training record ready to share |
NO PROTECTION IS PERFECT
How it works day to day
Once the policy and controls are in place, most of this runs quietly in the background.
- 1
Draft
Staff use approved AI tools for drafting, summarizing, and research as part of normal work.
- 2
Check
Technical controls scan for sensitive data heading to a tool that isn't approved, and block or flag it.
- 3
Review
A person reviews anything AI drafts before it goes to a client or gets used in a decision.
- 4
Report
If something gets flagged, your team sees what happened and can act on it quickly.
- 5
Refresh
The policy and approved tool list get reviewed on a regular schedule as new tools appear.
WHAT WE MEASURE
Three numbers you'll see every month.
We record a starting point during onboarding and report on these every month.
EVERY MEASURE IS TRACKED THROUGH THE CYBER6 PROVE FRAMEWORK
- Plan the goals
- Record the baseline
- Operate and observe
- Verify the results
- Evolve
PLAN THE GOALS
Approved tools in use
The share of AI activity happening in reviewed, approved accounts instead of personal ones.
RECORD THE BASELINE
Policy acknowledged
The share of staff who have read and signed off on the AI policy.
OPERATE AND OBSERVE
Blocked data-sharing attempts
How often sensitive data was caught heading to an unapproved tool, and what it was.
IN YOUR INDUSTRY
What changes in your industry
BEFORE
An associate pastes a client contract into a free chatbot to save time before a deadline.
AFTER
An approved drafting tool is set up so client data stays inside the firm's own account.
Law firms pageWHY CYBER6
Why Cyber6 for safe AI use
01
We manage the guardrails, not just write the policy
The same team that writes your AI policy also sets up the technical controls that catch mistakes, so the rules actually hold.
02
Plain language, real examples
Our policies use your business's own situations instead of generic legal language nobody reads.
03
We don't default to banning AI
We help you keep the tools that save real time and add guardrails only where the risk is real.
04
One partner across policy, protection, and training
The same team handles the policy, the technical controls, and the staff training, without another vendor to manage.
QUESTIONS
Questions people ask
We don't usually recommend it. Banning AI pushes the risk underground, since staff often keep using personal accounts anyway. A clear policy with real guardrails works better.
It depends on the tool's terms and how it's configured. Business versions of common AI tools can be set up so your data isn't used to train the model. We review your specific tools during the assessment.
Often yes, with the right setup and a person reviewing the output before it goes to a client. We help you figure out where that line is for your business.
Many everyday tools have added AI features recently. We review those as part of the assessment, since they're easy to overlook.
We write the plain-language version your staff will actually read. We recommend your legal counsel review the final policy, especially for regulated industries.
No technical control stops that completely. That's why training and a clear policy matter as much as the technical guardrails.
No. The goal is to keep the tools that are working and add guardrails only where the risk is real.
A first policy and basic controls are usually in place within a few weeks. Training and refinement continue after that.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
You're here
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
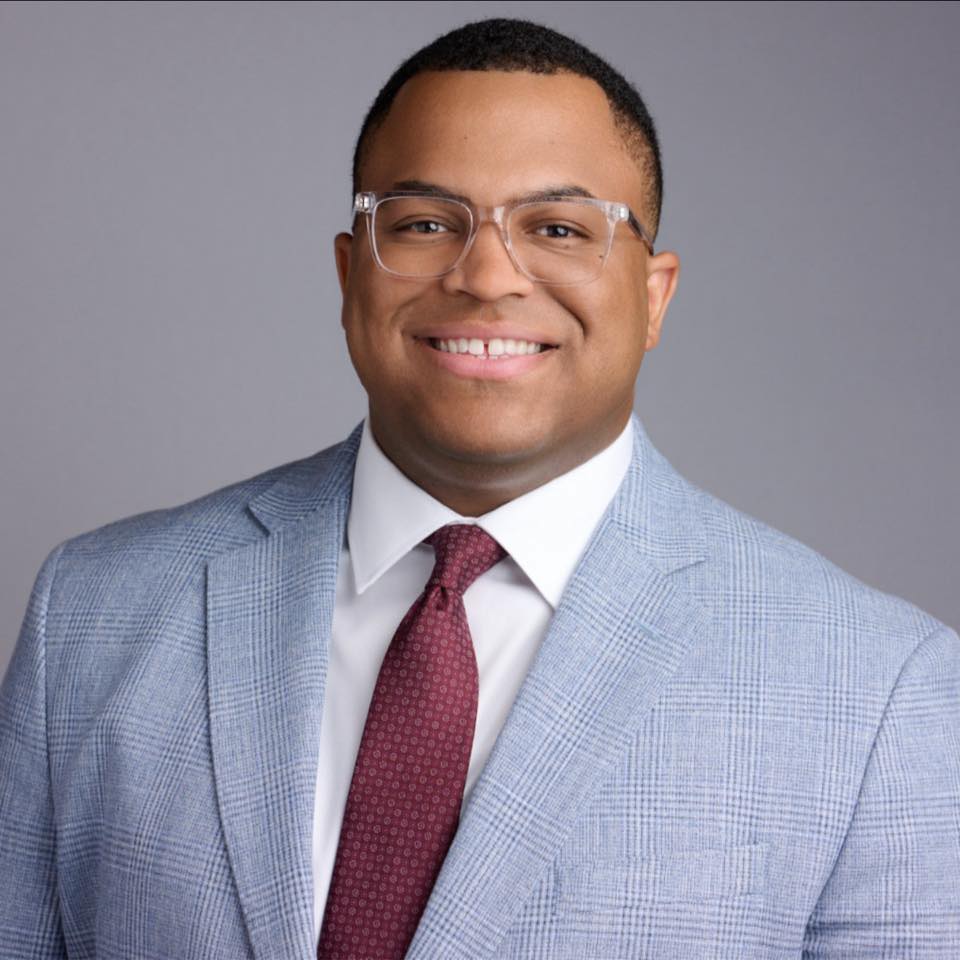
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's put guardrails around the AI use you already have.
A 30-minute call. No cost, no pressure, and honest answers.