
SOLUTION · TRAINING
Security awareness.
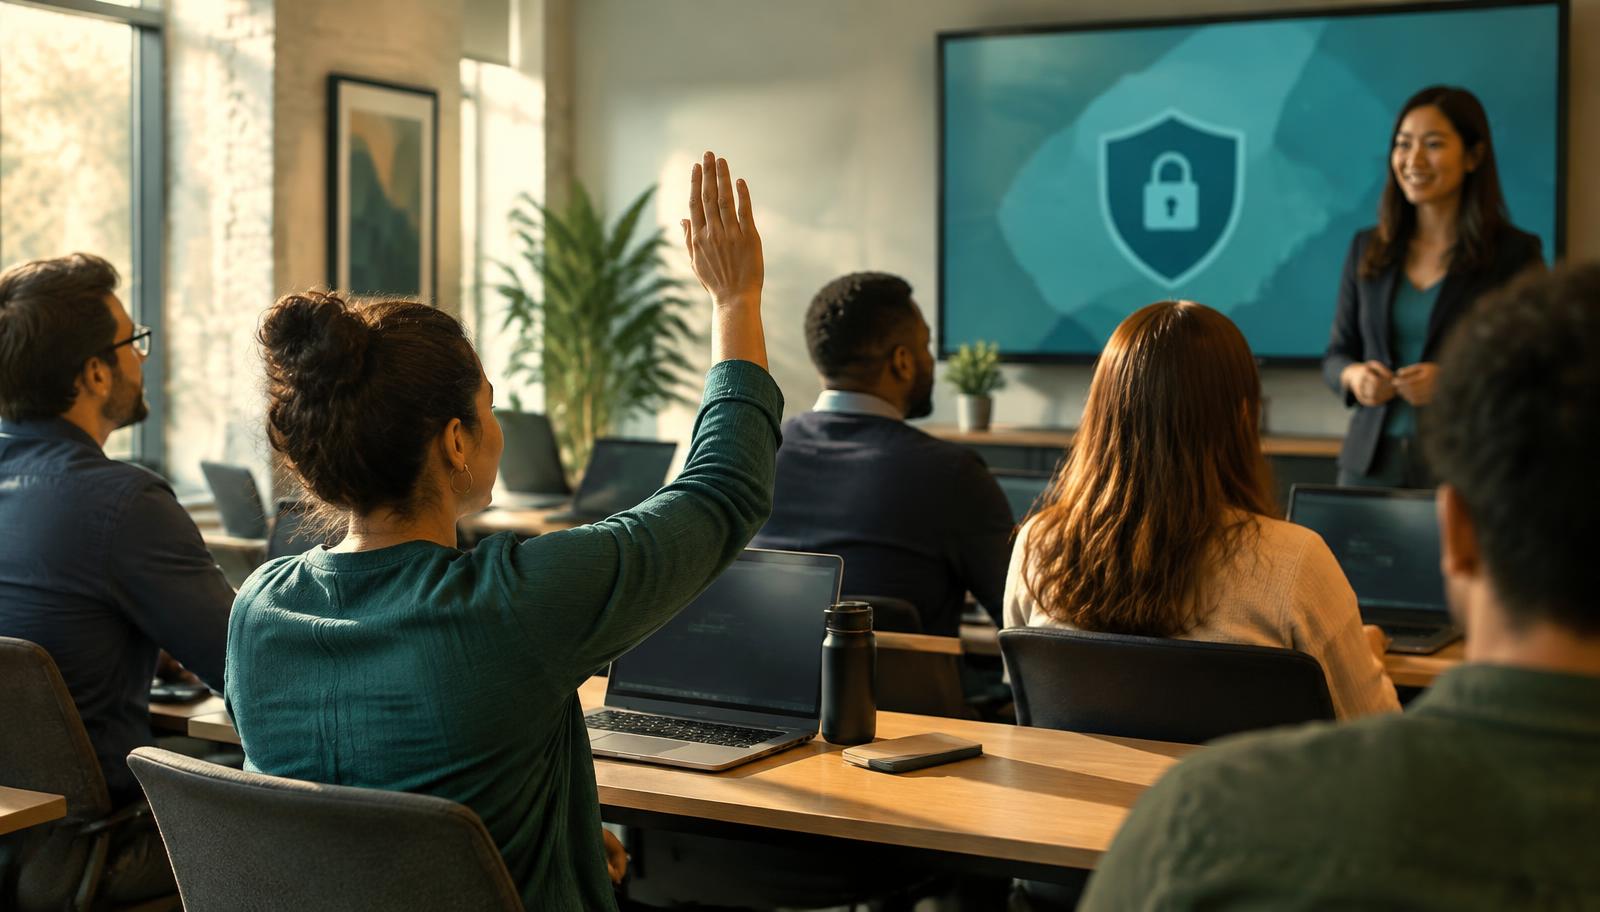
Most break-ins start with a normal-looking email that one person clicks. Cyber6 trains your team to spot those emails and gives them an easy way to report the ones that get through.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
WHAT'S REALLY HAPPENING
How a click turns into a breach
It rarely looks like an attack. It looks like a normal email on a busy afternoon.
STEP 01
A convincing email arrives
It looks like it's from a vendor, a bank, or someone inside the company. The writing is clean, and nothing looks obviously wrong.
STEP 02
Someone clicks under time pressure
Busy, distracted, or in a hurry, one person clicks the link or opens the attachment without checking closely.
STEP 03
The attacker gets in quietly
The stolen password opens the mailbox. Nothing looks different from the outside, so nobody notices right away.
STEP 04
The access spreads from the inside
The attacker sends convincing emails from that real mailbox to coworkers and vendors, using the trust already built into those relationships.
STEP 05
Nobody reports it in time
The person who clicked is worried about getting in trouble, so they stay quiet. The delay gives the attacker more time to do damage.
WHY IT HAPPENS
Four gaps sit behind almost every successful phishing email.
Select a cause to see the problems it creates on an average day.
- Training happens once a year, if at all: A single onboarding video is the only security training most staff ever get, and it's forgotten within months. Leads to: Missed threats, Repeat clicks, Wasted training.
- Nobody has tested what staff would actually do: Without a real phishing simulation, you're guessing whether your team would click, and guessing who needs extra help. Leads to: Missed threats, Repeat clicks, Wasted training.
- Reporting feels risky instead of normal: When staff worry about getting in trouble, they stay quiet about a click instead of raising a hand, and the delay costs you time. Leads to: Slow reporting, Hidden mistakes, Wire fraud risk.
- The people attackers target most get generic training: Finance staff and executives are the most valuable targets, but they often get the same generic module as everyone else. Leads to: Wire fraud risk, Missed threats, Hidden mistakes.
A single onboarding video is the only security training most staff ever get, and it's forgotten within months.
Missed threatsRepeat clicksWasted training
WHO IT HITS HARDEST
Where a lack of training hurts the most.
SCENARIO
Finance teams
A single convincing email to the right person can redirect a real payment before anyone double-checks it.
Finance teams
A single convincing email to the right person can redirect a real payment before anyone double-checks it.
Front desk and administrative staff
They handle the highest volume of email and calls, making them a frequent first target for an attacker.
Medical practices
A single clicked email can expose patient records and trigger a breach notification obligation.
Industry pageNonprofits
Volunteer and lean staff often have the least security training and the most donor data to protect.
Industry pageSIGNS THIS IS HAPPENING TO YOU
Six questions show how ready your team is.
One question at a time. The gauge moves as you answer.
Has your team had security training in the last year, beyond onboarding?
EXPOSURE
0 gaps so far
This runs in your browser only. Nothing you choose is sent anywhere.
WHAT IT'S COSTING YOU
One click adds up to real losses.
LINE ITEM
CATEGORY
- 01RISK
One mailbox becomes many
Attackers use a single hijacked account to send convincing emails to coworkers, vendors, and customers, spreading the damage fast.
- 02MONEY
Wire fraud and financial loss
A single well-timed, convincing email to the right person can redirect a real payment before anyone notices.
- 03TIME
Recovery time and cost
Even a contained incident takes hours or days of investigation, password resets, and cleanup.
- 04COMPLIANCE
Insurance and compliance gaps
Many cyber insurers require documented security training. Without it, a claim can be questioned or coverage can be harder to get.
- 05REPUTATION
A culture of hiding mistakes
When reporting feels risky, problems get discovered later and cost more to fix.
HOW CYBER6 FIXES IT
Training and an easy report button do most of the work.
Training for Businesses & Individuals does most of the work here. IT & Cybersecurity closes the loop when something gets through. Select any piece to see what it does.
TRAINING
Realistic phishing simulations
Test emails modeled on real attacks your team is likely to see, with private feedback showing people what they missed and why.
WHAT IT MEANS FOR YOUYour team practices spotting a fake before a real one arrives.
IT & CYBERSECURITY
- TRAINING: Realistic phishing simulations. Test emails modeled on real attacks your team is likely to see, with private feedback showing people what they missed and why. Your team practices spotting a fake before a real one arrives.
- TRAINING: Short, recurring training. Training arrives in small pieces throughout the year, tied to real scams and current events, instead of one long annual video. The lessons stick because they're short and repeated.
- TRAINING: Role-based training. Finance staff learn to verify payment changes by phone. Executives learn how they're impersonated. New hires learn the basics before they touch a real inbox. Training matches the actual risk each role faces.
- TRAINING: A security culture program. A network of security champions across departments and a regular newsletter keep the topic visible year-round, not just during one campaign. Security becomes part of how the team works, not a once-a-year event.
- IT & CYBERSECURITY: An easy, tracked way to report. One button or address to report a suspicious message, reviewed quickly, with no blame for reporting something that turns out to be fine. You find out about real threats faster because people aren't afraid to say something.
WHAT'S INCLUDED
Six pieces, running on a regular schedule.
Set up in this order, then run continuously so the habit doesn't fade.
01
Baseline test
A first phishing simulation shows where your team stands today, without any warning.
02
Monthly training
Short modules go out every month, built around current scams and real events.
03
Role-based sessions
Finance, executives, and new hires get training matched to how attackers target them.
04
One-click reporting
A simple button or address for anyone to report a suspicious message.
05
Regular simulations
Realistic phishing tests continue on a schedule, with private feedback after each one.
06
Quarterly report
Click rates, report rates, and trends by department, so you can see progress.
BEFORE AND AFTER
A phishing email, two ways.
| A typical Monday without Cyber6 | A typical Monday with Cyber6 |
|---|---|
| One video a year, then forgotten | Short training throughout the year |
| No idea who would click a fake email | Tracked click and report rates by department |
| Reporting feels risky | Reporting is easy, fast, and normal |
| Finance gets the same training as everyone else | Role-based training for the people attackers target most |
| Security is IT's job alone | A culture with champions across departments |
| A phishing test has never been run | Regular, realistic simulations with private feedback |
| A click goes unreported for days | A click gets reported and reviewed within minutes |
NO PROTECTION IS PERFECT
If someone clicks anyway
No training program can promise nobody ever clicks. What matters is how fast it's reported and contained.
- 1
Detect
A trained employee notices something is off and reports it through the one-click tool.
- 2
Contain
The affected account is disabled or reset quickly, before an attacker can do more with it.
- 3
Recover
Passwords are reset, mail rules and forwarding are checked, and access is reviewed.
- 4
Report
Leadership gets a plain account of what happened and what was affected.
- 5
Learn
The specific email or tactic used becomes the next training example, so the whole team learns from it.
WHAT WE MEASURE
Four numbers you'll see every quarter.
We record a starting point during onboarding and report on these on a regular schedule.
EVERY MEASURE IS TRACKED THROUGH THE CYBER6 PROVE FRAMEWORK
- Plan the goals
- Record the baseline
- Operate and observe
- Verify the results
- Evolve
PLAN THE GOALS
Click rate
The share of staff who click a simulated phishing email.
RECORD THE BASELINE
Report rate
The share of staff who report a suspicious email instead of ignoring or clicking it.
OPERATE AND OBSERVE
Time to report
How long it takes from a message arriving to someone reporting it.
VERIFY THE RESULTS
Repeat clicks
How many staff click more than once across simulations, showing where extra training is needed.
IN YOUR INDUSTRY
What changes in your industry
BEFORE
Staff, students, and families all share the same systems, and one clicked email can expose records.
AFTER
Short training and simulations run across staff, with role-based sessions for the people handling records.
Education pageWHY CYBER6
Why Cyber6 for security awareness
01
Practice, not punishment
Phishing simulations are framed as building a skill. Anyone who clicks gets private feedback, not a public callout.
02
Short and repeated, not long and forgotten
Monthly training in small pieces is easier to remember than one long session nobody finishes.
03
Training matched to the actual target
Finance and leadership get training built around how they're specifically impersonated, not a generic module.
04
One partner that also contains the breach
The same team that trains your staff also monitors accounts and responds if something gets through.
QUESTIONS
Questions people ask
The goal is practice, not punishment. Anyone who clicks gets brief, private feedback, not a public callout, and we frame the whole program as building a skill, not catching people out.
Short modules go out monthly, with phishing simulations on a regular schedule throughout the year, rather than one long session annually.
Yes. Executives and finance staff are frequently the most targeted, because a message that looks like it's from them, or to them, carries more weight.
They get immediate, private feedback explaining what they missed. Nobody is disciplined for a training exercise.
No. Training loses its effect quickly if it stops. This is an ongoing program with regular touchpoints.
Reports show trends by department and role so you know where to focus. They're meant to guide training, not to single out individuals.
Yes. Filters catch most bad emails, but some convincing ones always get through. Training is what catches the rest.
Most teams see a noticeable drop after the first two or three rounds of simulations and training, though the exact pace depends on your starting point.
Yes. New hires get onboarding-level training right away and are folded into the regular schedule from there.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
You're here
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
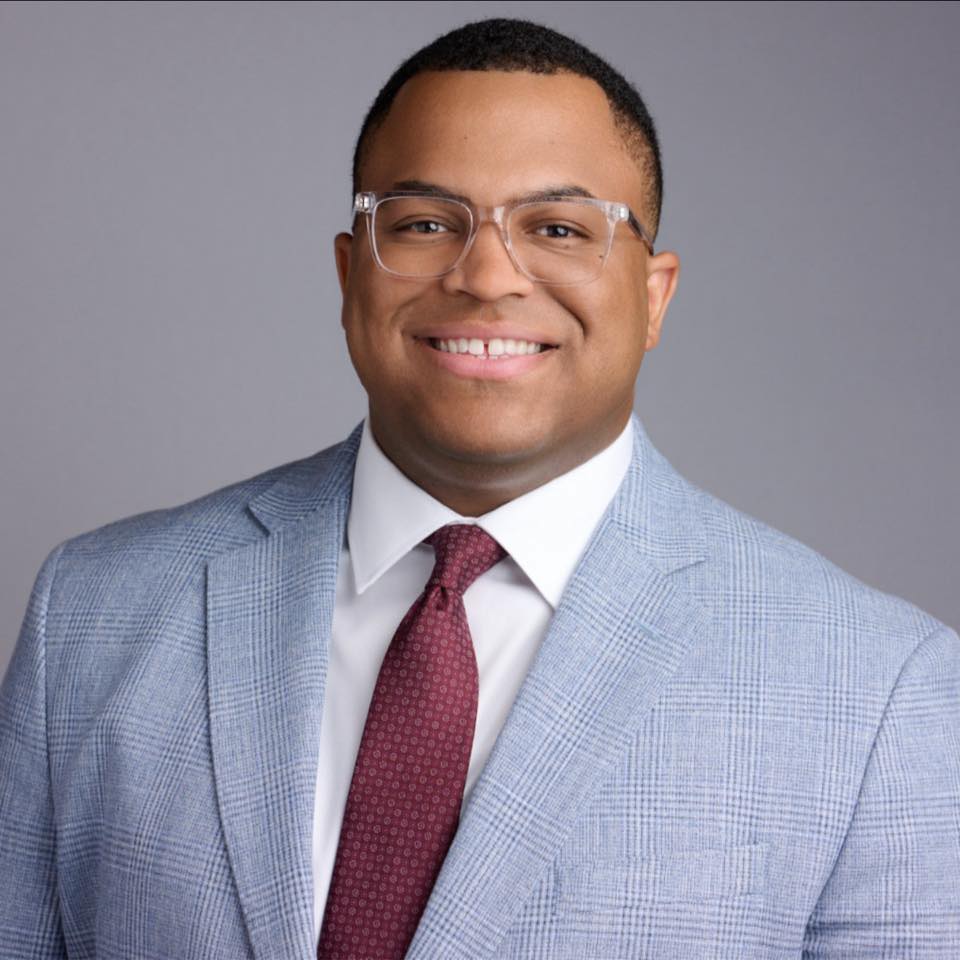
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's make your people your strongest defense.
A 30-minute call. No cost, no pressure, and honest answers.