
IT & CYBERSECURITY SOLUTIONS
IT that works and security that holds up.
Reliable support for the technology your business runs on, and layered protection against the attacks that actually hit small and midsize organizations. Aligned to the NIST Cybersecurity Framework and built around your real risks.
Dealing with an incident right now? Get urgent help
NIST CYBERSECURITY FRAMEWORK 2.0
WHICH ONE SOUNDS LIKE YOU?
What's keeping you up at night?
Stop ransomware and data loss
Layered protection, 24/7 monitoring, and backups you can recover from.
Jump to details ↓Prevent email and wire fraud
Catch fake invoices and payment requests before money moves.
Jump to details ↓Meet compliance requirements
HIPAA, CMMC, SOC 2, and more, explained, with help getting ready.
Jump to details ↓Qualify for cyber insurance
Put the controls insurers require in place, and prove it.
Jump to details ↓
THE SOLUTIONS
What we do about it, one problem at a time.
01 / 05 · Get reliable IT support
Solution 1 of 5
Get reliable IT support
“Our computers keep breaking, and nobody gets back to us.”
A support ticket moving through four steps: Reported, Assigned, Fixed, and Confirmed.
What we do
- You get a help desk with real people to call for everyday problems, from passwords to printers to new laptops.
- We manage and update your computers and accounts so fewer things break in the first place.
- New hires get set up and departing staff get removed on a clear checklist.
What changes
Problems get fixed instead of piling up. Your team stops losing time to the same issues every week.
Learn more about get reliable it supportSolution 2 of 5
Stop ransomware and data loss
“If our systems went down tomorrow, the business would stop.”
Four protection layers drawn as nested rings: Devices, Accounts, Backups, and Monitoring. An attack is stopped at the outer layers, and a Restored circle completes the loop.
What we do
- We protect every device with endpoint detection and response (EDR), software that spots and stops attacks on laptops and servers.
- We keep encrypted backups and test that they actually restore.
- We watch for warning signs with monitoring, and we follow a written plan when something goes wrong.
What changes
An attack becomes a bad day instead of a business-ending event. You know your data can come back because the restore has been tested.
Learn more about stop ransomware and data lossSolution 3 of 5
Prevent email and wire fraud
“We almost paid a fake invoice, and we're not sure we'd catch the next one.”
An email arrives and its warning signs highlight one by one: a look-alike domain, an urgent tone, and changed bank details. Then it is moved to quarantine.
What we do
- We filter email to catch fake senders, look-alike domains, and suspicious payment requests.
- We train your team with realistic practice emails.
- We help you set a simple rule: payment changes get verified by phone, using a number you already have.
What changes
Fake invoices get caught before money moves. Your team knows what to look for and what to do when something feels off.
Learn more about prevent email and wire fraudSolution 4 of 5
Meet compliance requirements
“A regulator, auditor, or big customer is asking questions we can't answer.”
HIPAA: Health privacy law for covered entities and their business associates.
A list of rules and standards. Choose one to see a one-line description.
What we do
- We explain which rules apply to you in plain language and find the gaps between where you are and what's required.
- We write the policies, put the controls in place, and collect the evidence auditors ask for.
- We prepare you for your audit or assessment and stay with you through it.
What changes
You can answer a regulator's or customer's questions with documents instead of guesses. Audits stop being a scramble.
Some certifications, like SOC 2 reports and CMMC certification, can only be issued by independent assessors. We get you ready, and we work alongside them.
Learn more about meet compliance requirementsSolution 5 of 5
Qualify for cyber insurance
“Our insurer sent a questionnaire, and we don't know how to answer it honestly.”
An insurance questionnaire with five checkboxes that fill one by one, each linked to a piece of evidence.
What we do
- We walk through your insurer's questionnaire with you and answer it accurately.
- We put commonly required controls in place, like multi-factor authentication (MFA), EDR, tested backups, staff training, and an incident response plan.
- We gather the evidence so you can show the controls exist, not just say they do.
What changes
You can answer the questionnaire honestly. You're in a stronger position at renewal.
Coverage decisions and premiums are up to your insurer. We can't guarantee either.
Learn more about qualify for cyber insurance
MATURITY
Where does your security stand today?
These four levels come from the NIST (National Institute of Standards and Technology) Cybersecurity Framework.
WHAT THIS LOOKS LIKE · PARTIAL
Security gets handled case by case, usually after something breaks.
WHAT WE'D DO FIRST
Find out what you have and where your biggest risks are.
MORE PROBLEMS WE SOLVE
Not on the list? We likely handle it.
Business continuity
If our systems went down, we'd lose days of work.
Handled by: Stop ransomware and data lossVendor risk
Our vendors have our data, and we don't know how they protect it.
Handled by: Meet compliance requirementsCloud migration
We're moving to the cloud and don't want to break anything.
Handled by: Cloud security
QUESTIONS
Questions owners ask us.
Yes. We offer co-managed services that support in-house IT teams, and white-label services for IT providers.
Yes. We sign business associate agreements (BAAs) for HIPAA and data processing agreements (DPAs) where needed.
No one honestly can. We close the gaps, prepare the evidence, and stay with you through the audit.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Automate · AI & Automation
The automations we build run on accounts and data we secure and watch.
Explore AutomateProtect · IT & Cybersecurity
Each IT & cybersecurity solution is built around your real risks and aligned to the NIST Cybersecurity Framework.
You're here
Empower · Training for Businesses & Individuals
Your team learns to spot fake emails and handle data safely, so the safeguards hold.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
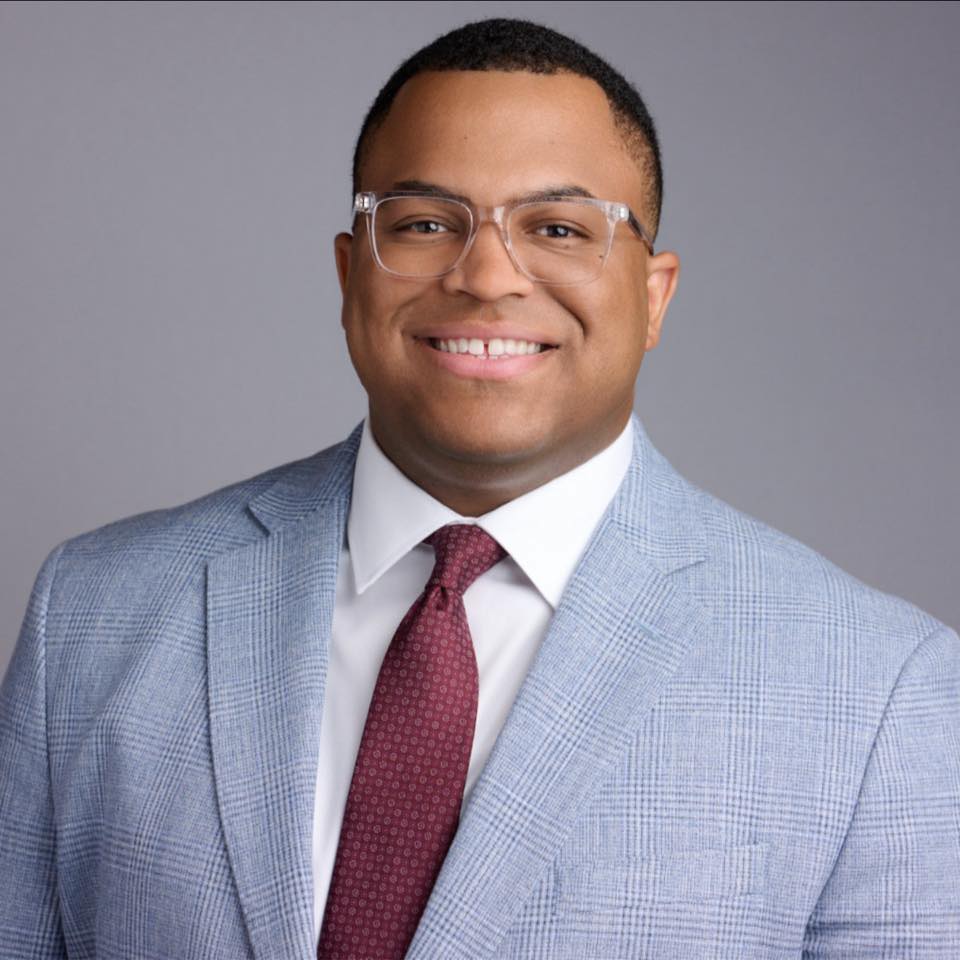
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's find your biggest risk first.
A 30-minute call. No cost, no pressure, and honest answers.