
IT & CYBERSECURITY · PENETRATION TESTING
Find the way in before someone else does.
Cyber6 testers try to get into your systems the way a real attacker would, with your permission, then hand you a plain report you can act on and check the fixes afterward.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
THE PROBLEM
You won't know it's open until someone walks through.
Three years ago, a contractor set up remote access for an old accounting system. The system was retired. The remote access was not. It is still there, reachable from the internet, with a password nobody remembers setting.
Your scans show hundreds of warnings every month, most of them low priority. Nobody has time to work out which ones actually matter, so they sit in a report nobody reads.
An attacker doesn't read the report. They try the forgotten door, find it open, and use it to move from one system to the next until they reach the files that matter.
WHAT IT'S COSTING YOU
Forgotten doors stay open
Old accounts, test systems, and remote access left behind are among the most common ways attackers get in.
Scan results nobody trusts
Automated scans list problems without proving which ones an attacker could actually use, so the important ones get lost.
Deals and renewals on hold
Customers, insurers, and frameworks increasingly ask for a recent test before they sign or renew.
Fixes that were never checked
A fix that looked right but didn't work leaves the same door open with a false sense of safety.
HOW IT WORKS
How a penetration test works
Nothing is tested without written permission, agreed boundaries, and a contact at your business who knows it is happening.
STEP 1
Agree the scope
We agree exactly which systems, addresses, and applications are in bounds, when testing happens, and who to call if something unexpected comes up.
STEP 2
Map what is exposed
Testers look at your business the way an attacker would, finding every system and login page they can reach.
STEP 3
Try to get in
Testers attempt to break in using the same methods real attackers use, carefully and without damaging your systems.
STEP 4
Prove what matters
Every finding comes with evidence showing how it was found and what an attacker could do with it.
STEP 5
Report in plain language
You get a report with each issue rated by risk, explained clearly, and paired with specific steps to fix it.
STEP 6
Retest the fixes
After your team or ours makes the fixes, we test again to confirm each door is actually closed.
Agree the scope
Map what is exposed
Try to get in
Prove what matters
Report in plain language
Retest the fixes
WHAT'S INCLUDED
Six parts of a test you can actually act on.
Three kinds of testing, and three things you walk away with.
- 01
Step 1: External testing
Everything an attacker can reach from the internet: your website, email, remote access, firewalls, and any forgotten systems.
WHAT IT MEANS FOR YOU
You know what the outside world can see and whether it can get in.
- 02
Step 2: Internal testing
What someone could do from inside your network, or with one stolen employee login, and how far they could get.
WHAT IT MEANS FOR YOU
You see how much damage one clicked email could lead to.
- 03
Step 3: Web application testing
Your customer portals, booking systems, and web applications tested for weaknesses in logins, data handling, and access.
WHAT IT MEANS FOR YOU
Customer data in your apps is checked before someone else checks it.
- 04
Step 4: Findings report
Every issue found, how it was found, and proof, written so both your technical staff and your leadership can follow it.
WHAT IT MEANS FOR YOU
No guessing about what the test actually found.
- 05
Step 5: Risk ratings and fix guidance
Each finding is ranked by risk and paired with clear steps to fix it, so you know what to work on first.
WHAT IT MEANS FOR YOU
Your time goes to the fixes that matter most.
- 06
Step 6: Retest
A second round of testing on each finding after it has been fixed, with an updated report confirming the result.
WHAT IT MEANS FOR YOU
You have proof the doors are closed, not just a promise.
IN YOUR INDUSTRY
What it looks like in your industry
BEFORE
An enterprise customer asks for a recent application test before renewal, and the last one was done two years and many releases ago.
AFTER
A web application test covers the current product, findings are fixed and retested, and the customer receives a clean summary.
WHAT WE MEASURE
What we measure
Each test gives you a baseline. Later tests show whether the same kinds of problems keep coming back.
AIM: GOING DOWN
Findings by risk level
The number of confirmed weaknesses, grouped as critical, high, medium, or low, in each test.
AIM: GOING UP
Findings closed on retest
The share of findings confirmed fixed when we test again after your fixes.
AIM: GOING DOWN
Time to fix
How long it takes from the report arriving to critical and high findings being fixed.
AIM: GOING DOWN
Repeat findings
Weaknesses that show up again in a later test, which point to a process that needs changing.
QUESTIONS
Common questions
Testers work carefully and avoid anything that could damage your systems. We agree timing and boundaries in writing, and you have a contact throughout.
A scan lists possible problems automatically. A penetration test has people try to actually use them, proving which ones are real and how serious they are.
Many businesses test once a year and after major changes. Your framework, insurer, or customers may set a specific schedule.
Your team, our managed IT team, or both. The report gives clear steps either way, and the retest confirms the result.
The full report stays with you. We can provide a shorter summary that is suitable to share with customers or auditors.
For external testing, no. For internal testing, we agree a safe way to connect. For application testing, we may use test accounts.
Cyber6 is an AI & technology partner. We automate the work slowing businesses down, run and protect their IT, and train their people. Testing is part of the Protect work.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Automate · AI & Automation
Automations that collect customer information through forms and portals are tested like any other entry point.
Explore AutomateProtect · IT & Cybersecurity
Penetration testing proves which of your protections hold, and which ones don't.
You're here
Empower · Training for Businesses & Individuals
Findings from each test become real examples in your team's security training through Cyber6 Academy.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
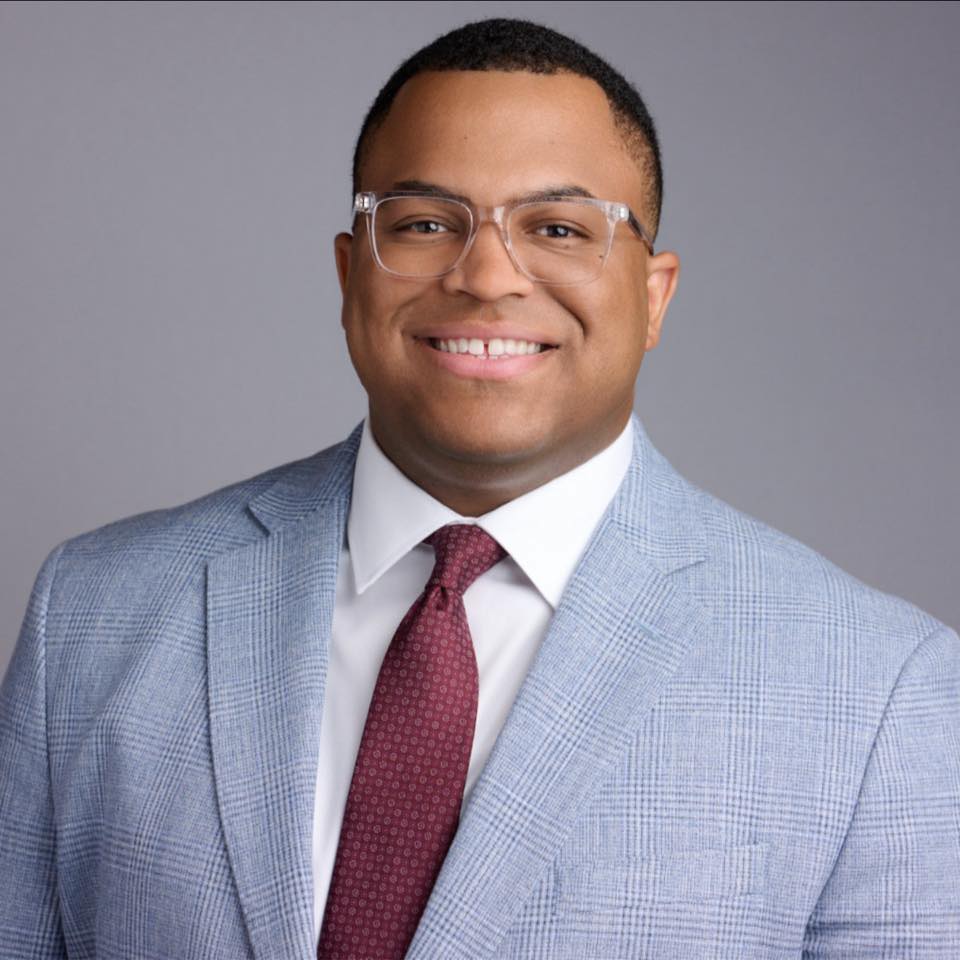
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's find the way in before anyone else does.
A 30-minute call. No cost, no pressure, and honest answers.