
IT & CYBERSECURITY · 24/7 MONITORING & RESPONSE
Someone is watching at 2am, and someone picks up the phone.
Alerts only help if a person acts on them. Cyber6 watches your systems around the clock, confirms what is real, and responds when something goes wrong, day or night.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
- 01
Detect
- 02
Contain
- 03
Investigate
- 04
Restore
- 05
Report
THE PROBLEM
Attacks don't wait for business hours.
It is Saturday night. Someone signs in to your bookkeeper's account from another country and starts setting up rules to forward invoices. Your security tools notice and send an alert.
The alert lands in a shared inbox nobody checks on weekends. Nothing else happens. By Monday morning, the attacker has read two days of email and sent a fake invoice to three of your customers.
The tools worked. They saw it. What was missing was a person to read the alert, decide it was real, and lock the account before the damage spread.
WHAT IT'S COSTING YOU
Hours become days
Every hour an attacker goes unnoticed gives them more time to spread, steal data, or prepare ransomware.
Downtime you can't bill for
When systems go down, staff sit idle and customers wait, and the cost grows with every hour of recovery.
Alert fatigue
Tools produce hundreds of warnings. Without someone to sort them, the real one gets lost among the false alarms.
No plan in the moment
Deciding who to call, what to shut off, and what to tell customers in the middle of a crisis leads to costly mistakes.
HOW IT WORKS
What happens when something goes wrong
Every step is agreed with you in advance, written down, and tested, so nobody is making it up at 2am.
STEP 1
Detect
An analyst reviews the alert, confirms whether it is real, and tells you what is happening in plain language.
STEP 2
Contain
Affected accounts and devices are isolated so the problem stops spreading, following the actions you pre-approved.
STEP 3
Investigate
We work out how they got in, what they touched, and whether anything else was affected.
STEP 4
Restore
Systems are cleaned and restored from tested backups, in an order that gets your most important work running first.
STEP 5
Report
You get a written account of what happened, what we changed, and what to fix next, ready for your insurer.
Detect
Contain
Investigate
Restore
Report
WHAT'S INCLUDED
Three commitments: watching, acting, and practicing for the worst day.
Monitoring finds the problem. The response retainer makes sure someone is ready to act on it.
- 01
Step 1: 24/7 monitoring and response
Analysts review alerts from your devices, email accounts, cloud services, and firewalls around the clock, and take action on the real ones.
WHAT IT MEANS FOR YOU
A threat on Saturday night is handled Saturday night, not Monday morning.
- 02
Step 2: Yearly plan review and practice run
Once a year we walk your leadership through a realistic scenario, test the plan against it, and update contacts and steps.
WHAT IT MEANS FOR YOU
The plan still matches your business when you actually need it.
- 03
Step 3: Incident response retainer
A named team, agreed response steps, and a written plan prepared before you ever need it, reviewed with you every year.
WHAT IT MEANS FOR YOU
On your worst day, you make one call and the plan starts.
Tools we use
- Monitoring
- Blumira
We connect monitoring to the systems you already run, and confirm coverage during onboarding.
IN YOUR INDUSTRY
What it looks like in your industry
BEFORE
Ransomware spreads across the plant network overnight, and the first sign is a stopped production line at 6am.
AFTER
Unusual activity on one computer is spotted overnight, that machine is cut off from the network, and the shift starts on time.
WHAT WE MEASURE
What we measure
We track these from the day monitoring starts and review them with you on a regular schedule.
AIM: GOING DOWN
Time to detect
How long it takes from suspicious activity starting to an analyst confirming it is a real problem.
AIM: GOING DOWN
Time to contain
How long it takes from confirmation to the affected account or device being isolated.
AIM: GOING DOWN
Alerts that needed you
How many alerts reached your team for a decision, compared with how many analysts handled on their own.
AIM: GOING UP
Monitoring coverage
The share of your devices, accounts, and cloud services actually sending information to the monitoring team.
BE READY
Your response plan covers
We write these down with you during onboarding, so they are settled before anything happens.
- Who at your business we call first, and who approves major actions
- Which accounts and devices we can isolate without asking
- Which systems come back first during recovery
- Your insurer's claim contact and notification requirements
- Who speaks to customers, staff, and regulators
- Where backups live and how often they are tested
QUESTIONS
Common questions
Real analysts. Software collects and sorts the alerts, and people decide what is real and what to do about it.
Only what you pre-approve in the response plan, such as locking a compromised account or isolating a laptop. Bigger decisions come to you first.
Yes. Monitoring watches those tools and acts on what they find. It works best with well-managed devices and tested backups underneath.
Right away for anything that needs a decision, and in a regular report for everything else. We agree the rhythm during onboarding.
Many insurers and contracts ask for continuous monitoring and a response plan. We provide documentation, and your insurer or contract officer makes the final call.
Tell us immediately. We'll help with what we can and be clear about what is and isn't covered yet.
Cyber6 is an AI & technology partner. We automate the work slowing businesses down, run and protect their IT, and train their people. Monitoring and response are part of the Protect work.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Automate · AI & Automation
Automations that alert customers and staff keep working after an incident, because recovery puts the most important systems back first.
Explore AutomateProtect · IT & Cybersecurity
The SOC is the layer that notices when everything else is bypassed, and acts on it.
You're here
Empower · Training for Businesses & Individuals
Tabletop exercises through Cyber6 Academy let your leadership practice the response plan before it is real.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
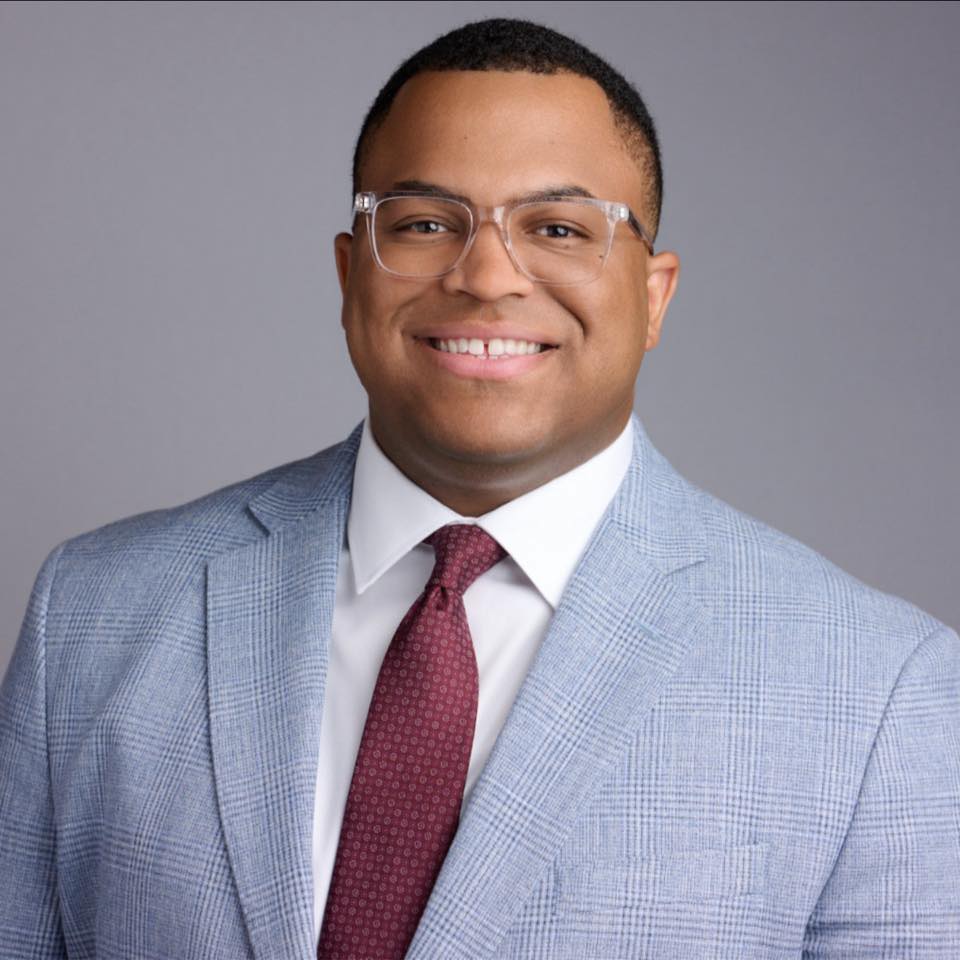
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's make sure someone is always watching.
A 30-minute call. No cost, no pressure, and honest answers.