
SOLUTION · IT & CYBERSECURITY
Vendor risk.
Every vendor with access to your data is a risk you don't fully control. Cyber6 builds the list of who actually holds your data, reviews the ones that matter most, and tracks findings until they close.
Cyber6 is an AI & technology partner: we automate the work slowing businesses down, protect them with IT & cybersecurity, and train their people.
WHAT'S REALLY HAPPENING
How a vendor's problem becomes your problem
It starts with a normal decision: signing up a vendor to solve a problem quickly.
STEP 01
A new vendor gets added
A billing service, a scheduling app, or a contractor is brought on because it solves a problem fast. Nobody reviews how it handles the data it will receive.
STEP 02
More vendors get added the same way
Over time, the list of vendors grows, each added under the same time pressure, with no one keeping track of who has access to what.
STEP 03
A customer asks a question you can't answer
A larger customer sends a security questionnaire asking how your vendors protect their data. Nobody has that information ready.
STEP 04
One vendor is breached
A vendor holding your customer or patient data has a security incident. The breach happened on their systems, not yours.
STEP 05
You're the one making the calls
You're now notifying customers or patients and answering questions, even though the breach happened somewhere else, because their data was in your vendor's hands.
WHY IT HAPPENS
Four gaps sit behind almost every vendor incident.
Select a cause to see the problems it creates over a normal year.
- No one keeps a full vendor list: Vendors are added department by department, and no single list shows who has access to what across the business. Leads to: No visibility, Slow response, Repeat gaps.
- Contracts are signed before security is reviewed: The vendor solves the immediate problem, and security review happens after the contract, if at all. Leads to: Uneven protection, Regulatory exposure, No visibility.
- Reviews happen once, then get forgotten: A vendor might get reviewed when first signed, but nobody checks again as the relationship or the data shared changes. Leads to: Repeat gaps, Uneven protection, Slow response.
- Findings sit in a folder instead of getting tracked: A review that isn't followed up on doesn't close anything. Gaps found once stay open indefinitely. Leads to: Repeat gaps, Regulatory exposure, Stalled contracts.
Vendors are added department by department, and no single list shows who has access to what across the business.
No visibilitySlow responseRepeat gaps
WHO IT HITS HARDEST
Where vendor risk hurts the most.
SCENARIO
Owners and office managers
They sign vendor contracts under time pressure and rarely have a security review built into that process.
Owners and office managers
They sign vendor contracts under time pressure and rarely have a security review built into that process.
Medical practices
Billing services and other vendors that touch patient data fall under the same expectations as the practice itself.
Industry pageSoftware companies
Enterprise customers increasingly send security questionnaires that ask exactly what a vendor review documents.
Industry pageDefense contractors
Subcontractor and vendor oversight is a named requirement in the frameworks these contracts depend on.
Industry pageSIGNS THIS IS HAPPENING TO YOU
Six questions show how exposed you are.
One question at a time. The gauge moves as you answer.
Can you produce a full list of vendors with access to your data?
EXPOSURE
0 gaps so far
This runs in your browser only. Nothing you choose is sent anywhere.
WHAT IT'S COSTING YOU
Unreviewed vendors add up to real exposure.
LINE ITEM
CATEGORY
- 01COMPLIANCE
A vendor breach can become your notification obligation
If a vendor holding your customer or patient data is breached, laws and contracts often still require you to notify the people affected.
- 02MONEY
Contracts stall without answers
Larger customers increasingly send security questionnaires before signing, and a slow or weak response can delay or lose the deal.
- 03RISK
No visibility means no control
Without a current list of vendors and their access, you can't act quickly when a vendor has its own security incident.
- 04RISK
Uneven protection across your data
Your own systems might be well protected while a vendor holding a copy of the same data is not, and overall risk is only as good as the weakest link.
- 05REPUTATION
Reputation on the line for someone else's mistake
Customers and patients associate the breach with you, even when the failure happened at a vendor.
HOW CYBER6 FIXES IT
A tracked list and regular reviews close the gap.
IT & Cybersecurity does most of the work here. Select any piece to see what it does.
IT & CYBERSECURITY
Build the list you don't have
We work with you to identify every vendor with access to your data or systems, what they can see, and how sensitive it is.
WHAT IT MEANS FOR YOUYou finally know who actually holds your data and what they can reach.
AI & AUTOMATION
TRAINING
- IT & CYBERSECURITY: Build the list you don't have. We work with you to identify every vendor with access to your data or systems, what they can see, and how sensitive it is. You finally know who actually holds your data and what they can reach.
- IT & CYBERSECURITY: Rank vendors by what's at risk. Not every vendor needs the same level of scrutiny. We rank vendors by how much access they have and how sensitive the data is. You focus time on the handful of vendors that matter most.
- IT & CYBERSECURITY: Review and document what matters. For high-risk vendors, we review security evidence like a completed questionnaire, and note the gaps, such as missing multi-factor authentication. You have a documented answer when someone asks how a vendor protects your data.
- IT & CYBERSECURITY: Track findings until they close. A review that sits in a folder doesn't fix anything. We track findings and follow up until vendors close them. Gaps get closed instead of reviewed once and forgotten.
- IT & CYBERSECURITY: Strengthen contracts going forward. We provide guidance on the data protection and breach notification language to look for in new vendor contracts. New vendors start with clearer expectations instead of none.
- AI & AUTOMATION: Automatic review reminders. Each vendor gets a re-review date. Reminders and evidence requests go out on schedule without anyone keeping a calendar. Reviews happen on time instead of when someone remembers.
- TRAINING: Buyer checklist for new vendors. Staff who sign up for new tools learn the few questions to ask before a vendor gets access to your data. New vendors get checked before they're in, not after.
WHAT'S INCLUDED
Six pieces, built in the order that closes the biggest gaps first.
Set up in this order once we understand which vendors touch your most sensitive data.
01
Vendor discovery
We work with you to build the initial list of vendors and what each one can access.
02
Risk ranking
Vendors are ranked by access and data sensitivity, so review effort goes where it matters.
03
High-risk reviews
We collect and review security evidence from your highest-risk vendors.
04
Finding tracking
Open findings are tracked with a status and a follow-up date.
05
Contract guidance
We recommend data protection language for new and renewing vendor contracts.
06
Scheduled re-review
Vendors are reviewed again on a regular schedule, not just once.
BEFORE AND AFTER
A vendor relationship, two ways.
| A typical Monday without Cyber6 | A typical Monday with Cyber6 |
|---|---|
| No list of who has your data | A documented, current list of vendors and their access |
| All vendors treated the same | Vendors ranked by risk, with review effort focused on the highest ones |
| Security reviewed after signing, if ever | Security reviewed before a contract is signed |
| Findings noted once and forgotten | Findings tracked until closed |
| No answer to a customer's security questionnaire | Documented evidence ready to share |
| Vendor contracts silent on data protection | Contracts with data protection and notification language |
NO PROTECTION IS PERFECT
If a vendor is breached anyway
No review can guarantee a vendor never has an incident. What matters is how fast you know and how ready you are to act.
- 1
Detect
A vendor notifies you of a breach, or monitoring flags unusual vendor activity.
- 2
Contain
Access from the affected vendor is limited or paused while the situation is assessed.
- 3
Recover
We help confirm what data was exposed and work with you on next steps with that vendor.
- 4
Report
We help you meet any notification requirements to customers, patients, or regulators.
- 5
Learn
We update the vendor's risk rating and review whether the relationship should continue.
WHAT WE MEASURE
Four numbers you'll see every review cycle.
We record a starting point during onboarding and report on these on a regular schedule.
EVERY MEASURE IS TRACKED THROUGH THE CYBER6 PROVE FRAMEWORK
- Plan the goals
- Record the baseline
- Operate and observe
- Verify the results
- Evolve
PLAN THE GOALS
Vendors identified
The total number of vendors with access to your data or systems.
RECORD THE BASELINE
Vendors reviewed
The share of high-risk vendors with a completed security review on file.
OPERATE AND OBSERVE
Open findings
The number of documented gaps still waiting on a vendor or a decision.
VERIFY THE RESULTS
Findings closed
How many previously open findings were resolved since the last review.
IN YOUR INDUSTRY
What changes in your industry
BEFORE
A billing service holds patient records, and nobody has checked how it protects them.
AFTER
The vendor is reviewed, findings are tracked, and the relationship is documented.
Medical practices pageWHY CYBER6
Why Cyber6 for vendor risk
01
We build the list most businesses don't have
Most companies underestimate how many vendors actually touch their data until we map it out together.
02
Effort goes where the risk actually is
Not every vendor gets the same scrutiny. We focus review time on the ones holding your most sensitive data.
03
Findings get tracked, not filed away
A review only matters if it leads to a closed gap. We follow up until it does.
04
One partner for the review and the response
If a vendor is ever breached, the same team that reviewed them helps you respond.
QUESTIONS
Questions people ask
No. We focus review effort on vendors with meaningful access to sensitive data or systems, and handle lower-risk vendors more lightly.
That's a finding in itself. We help you weigh the risk and decide whether to push for the information, add contract protections, or reconsider the relationship.
A compliance review usually looks at your own controls. Vendor risk specifically looks outward, at what you've handed to other companies and how well they protect it.
If you share customer or patient data with any outside vendor, the exposure exists regardless of size. Larger customers are also increasingly asking small vendors to prove this kind of oversight.
It depends on the vendor's risk level, but a common approach is reviewing high-risk vendors yearly and whenever their access or your data with them changes.
Yes. The same documentation this work produces about your own controls is usually what a customer questionnaire is asking for.
We help you weigh the options: work with the vendor to close the gap, add contract protections, limit what data they receive, or move to a different vendor.
Both. A vendor is anyone with access to your data or systems, whether that's a software company, a billing service, or a contractor.
We look at how much access a vendor has and how sensitive the data is. A payroll processor or a data storage vendor typically ranks higher than a office supply company.
WHO WE'VE WORKED WITH
- A statewide cybersecurity assessment program
- Credit unions
- A water and wastewater utility
- Housing organizations
- Nonprofits and churches
- Small businesses
- A health and wellness startup
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
One partner for all three.
Protect · IT & Cybersecurity
IT and cybersecurity, managed around the clock.
You're here
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
Explore Empower
WHY CYBER6
Why businesses choose Cyber6.
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
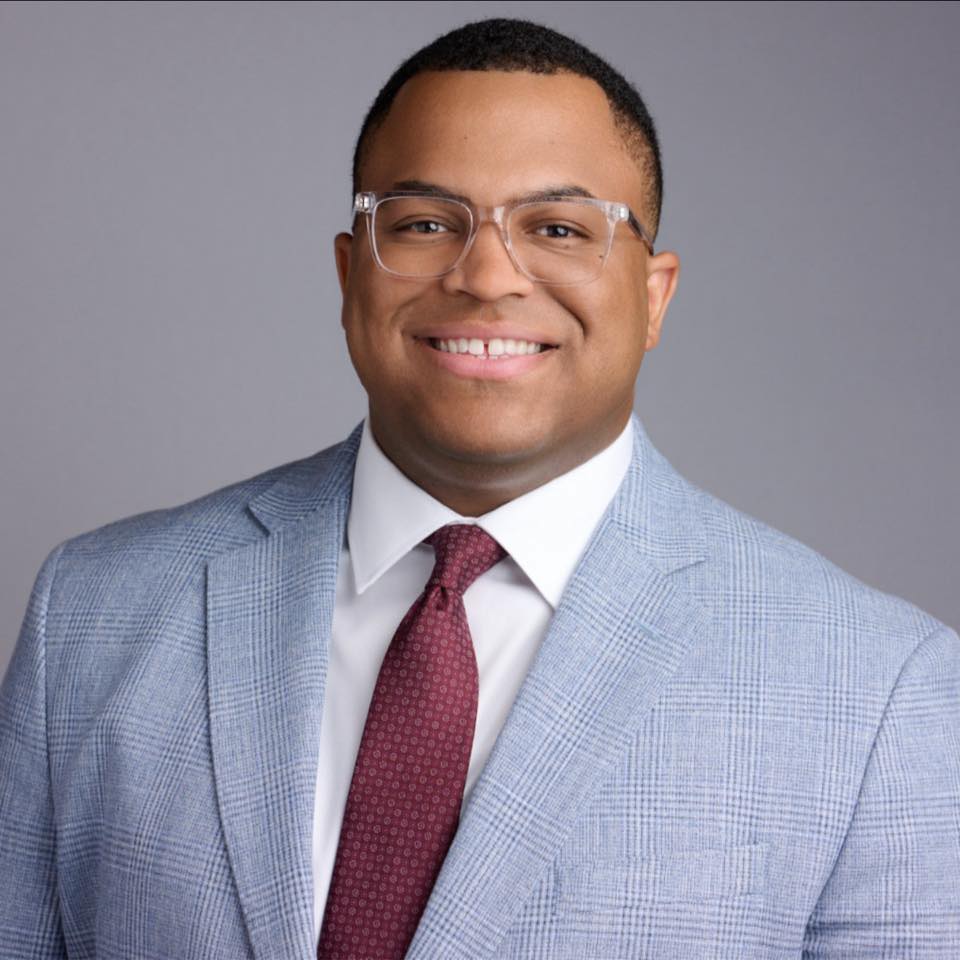
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Four steps from first call to results.
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
Let's find out who's really holding your data.
A 30-minute call. No cost, no pressure, and honest answers.