
Article
CMMC in plain English for small defense contractors
CMMC can sound like alphabet soup. Here is what Level 1 and Level 2 actually require, and where a small contractor should start.
- PROTECT
6 min ·
INDUSTRY / DEFENSE CONTRACTORS
A prime contract or a subcontract shows up with a CMMC requirement and a deadline, and someone has to figure out what your score actually is, what controlled unclassified information you're handling, and how far off you are. Cyber6 runs the gap assessment, builds the documentation, and gets your environment to where the contract needs it to be.
6 min read
CMMC readiness dashboard
WE GET IT
A contract clause you didn't expect
A flow-down clause in a subcontract requires a CMMC level you haven't planned for, with a deadline set by the prime, not by you.
Nobody knows the real SPRS score
Someone self-assessed against NIST SP 800-171 a while ago, entered a number into SPRS, and nobody's fully sure it still reflects reality.
Controlled unclassified information without a clear boundary
CUI from a contract lives in the same email inbox and file server as everything else, because nobody drew a line around where it's allowed to live.
The System Security Plan is a stale document
The SSP was written once, maybe by a consultant who's gone now, and hasn't been updated since your network changed.
The documentation burden falls on one person
The controls exist in fragments, but proving it to an assessor means one person assembling evidence from memory and old emails.
Email and file sharing weren't built for CUI
Standard commercial Microsoft 365 or Google Workspace wasn't built to the government cloud requirements CUI needs, and switching feels disruptive.
A subcontractor's weak security becomes your problem
You flow CMMC requirements down to your own subcontractors, but you have no way to verify they're actually meeting them.
72 hours to report an incident
DFARS 252.204-7012 requires rapid reporting to the DoD after a cyber incident involving covered defense information, and most contractors have never rehearsed that timeline.
THE IMPACT
The contract itself
Falling below the required CMMC level or SPRS score can mean losing eligibility for the contract, whether it's already awarded or still in the pipeline.
Time lost to a rushed assessment
Starting the gap assessment after the deadline is announced means working under pressure, at the pace the assessor requires, not the pace you'd choose.
Exposure from mishandled CUI
Controlled unclassified information sitting in an unprotected inbox or shared drive is a data exposure risk and a contract compliance failure at once.
The cost of getting it wrong twice
A System Security Plan or POA&M built without a real gap assessment often needs to be redone once an actual assessor or a prime's audit finds the gaps.
Future contract eligibility
A documented, current compliance posture is what lets you bid on the next contract without starting the whole process over.
COMPLIANCE
This is general information, not legal advice.
THE FIX
AUTOMATE
The right customers find you on Google, AI search, and social, in your own voice.
Every call, text, form, and quote turns into booked work.
Customers hear from you at the right time, without your team chasing them.
Money you've already earned comes in sooner, without awkward phone calls.
Less retyping and waiting, more time for the work that matters.
Proposal and documentation assistance
Compliance documentation, policies, and evidence are kept current and organized, so responding to a proposal request or an assessor takes minutes, not days.
POA&M tracking and reminders
Each milestone gets an owner and a due date, with automatic reminders before it slips, so the POA&M reflects real progress.
Subcontractor compliance tracking
Subcontractor attestations and evidence are collected and tracked in one place, with reminders sent automatically before they lapse.
PROTECT
We map your systems, data flows, and where controlled unclassified information lives, and score you against the CMMC level your contracts require, not a generic checklist.
What this means for you: You know your real starting point before an assessor or a prime does.
We write the SSP describing how each control is implemented, and the Plan of Action and Milestones for anything not yet in place, in the structure assessors expect.
What this means for you: You have the core documents an assessment or a prime's audit asks for first.
For contracts requiring it, we move email and file storage into Microsoft 365 GCC High, a government-community cloud environment built for handling CUI and export-controlled data.
What this means for you: Your CUI lives in an environment built for the requirement, not a workaround.
A oversees your program, tracks control implementation, and represents your security posture in conversations with primes and assessors.
What this means for you: You get security leadership without hiring a full-time compliance officer.
For contracts requiring it, we run penetration testing against your environment and document the results the way an assessor expects to see them.
What this means for you: You walk into a third-party assessment with evidence, not hope.
EMPOWER
Anyone who touches contract data
What counts as controlled unclassified information, where it's allowed to live, and how to mark and send it without creating a compliance gap or a security incident.
Program managers and IT leads
A walkthrough of the 72-hour DFARS reporting timeline, who calls the DoD, and what evidence needs to be ready, so it isn't figured out live during a real incident.
A DAY WITH CYBER6
Day 1PROTECT
The gap assessment maps every system touching CUI and scores you against your required CMMC level.
Day 4PROTECT
Multi-factor authentication is enforced across every account that can reach contract data.
Day 9PROTECT
The System Security Plan and POA&M are drafted, reviewed with your team, and signed.
Day 12EMPOWER
Staff who handle CUI complete training on where it's allowed to live and how to send it correctly.
YOUR TOOLS
We work alongside the systems you already use. We'll confirm what connects during your assessment.
QUESTIONS
The gap assessment recalculates your score against the actual state of your environment, not the self-assessment on file, so you know where you really stand.
It depends on the size of your environment and how many systems touch CUI, but most contractors get a clear picture within a few weeks.
It depends on your contract requirements and how you handle CUI. We review your specific obligations during the assessment before recommending a migration.
A Plan of Action and Milestones documents controls you haven't fully implemented yet and your timeline to close them. Most contractors need one, since few start at full compliance.
Yes. A vCISO oversees your program so you're not expected to have compliance expertise in-house.
DFARS requires reporting to the DoD within 72 hours of discovery. We build and rehearse that process ahead of time, so it's not improvised during an incident.
If you flow down CMMC requirements to them, yes. We can help you verify their posture as part of your own compliance program.
Nothing. It's a free review of your current score, your gaps, and what it takes to close them.
RESOURCES
CMMC can sound like alphabet soup. Here is what Level 1 and Level 2 actually require, and where a small contractor should start.
6 min ·
If you want to work with the Department of Defense, you must meet CMMC standards. Level 1 covers the basics of protecting Federal Contract Information.
6 min ·
The CompTIA Security+ is one of the most popular entry-level security certificates. Find out if it is the right choice for your career and what you need to know to pass.
7 min ·
Every result is measured against your own starting point.
How we prove it →PART OF ONE PARTNER
Protect · IT & Cybersecurity
IT and cybersecurity, managed around the clock.
You're here
Empower · Training for Businesses & Individuals
Training that builds skills for your team and your career.
Explore EmpowerWHY CYBER6
One partner, not three vendors
The people automating your work also run and protect your IT and train your team, so nothing falls between companies.
Plain language and real people
You talk to people who explain things clearly, answer the phone, and tell you what they'd do in your place.
Measured against your own numbers
We record where you start before anything changes, then report results against that baseline.
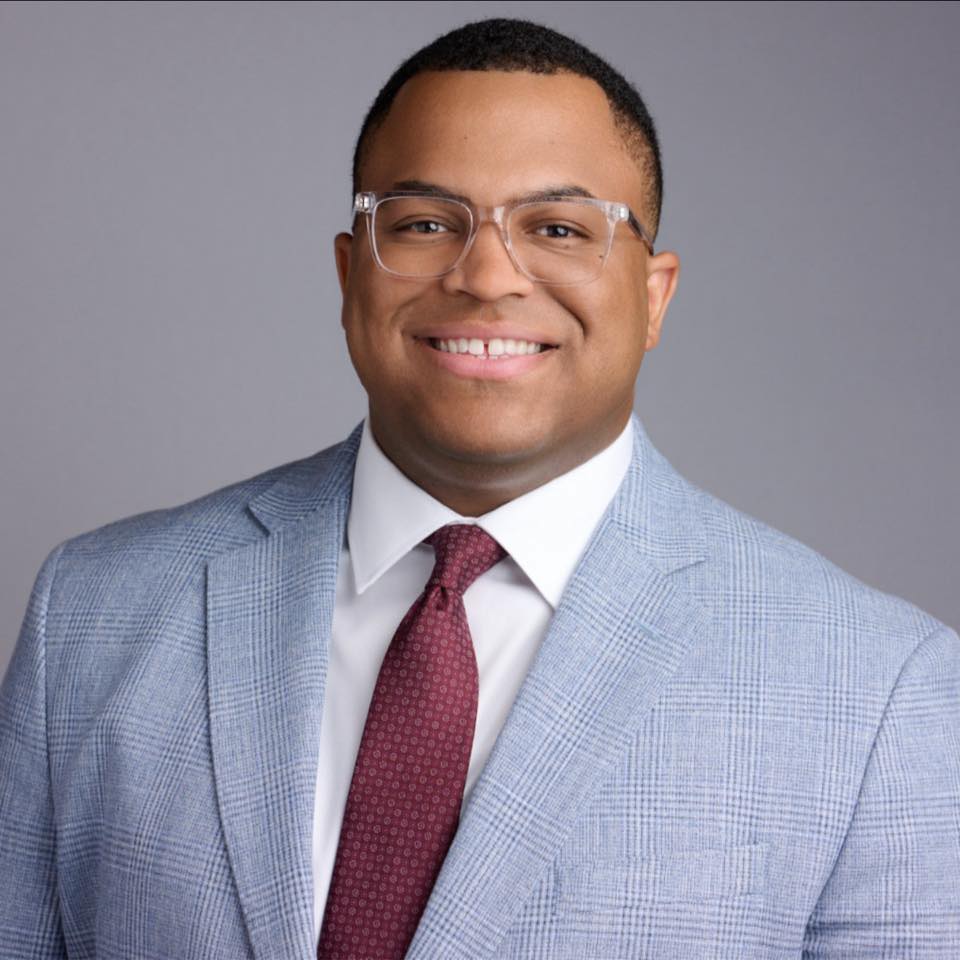
Marquis Carroll, Founder & CEO. Marquis has spent years doing hands-on IT and security work through his own business, and runs a mentorship program that has helped people start careers in tech.
Our storyGETTING STARTED
Explore
A relaxed 30-minute conversation about how your business runs and what's getting in the way. No cost, no pressure.
You get: honest answers on whether we can help.
Assess
We look at your systems, security, manual work, and training needs, and record your starting numbers.
You get: a plain-English picture of your risks and opportunities.
Set up
A prioritized plan and proposal, then a kickoff that introduces your team and sets up access safely.
You get: a shared timeline and who to call for what.
Enable
We roll out in phases, train your team, and walk you through your first results.
You get: your first plain-English report, measured with PROVE.
A 30-minute call. No cost, no pressure, and honest answers.